 Click main image to view in full screen.
SAMA ITGF Patch & Release Management Register – Excel XLSX
Excel (XLSX) Arabic


BENEFITS OF THIS DOWNLOADABLE EXCEL DOCUMENT
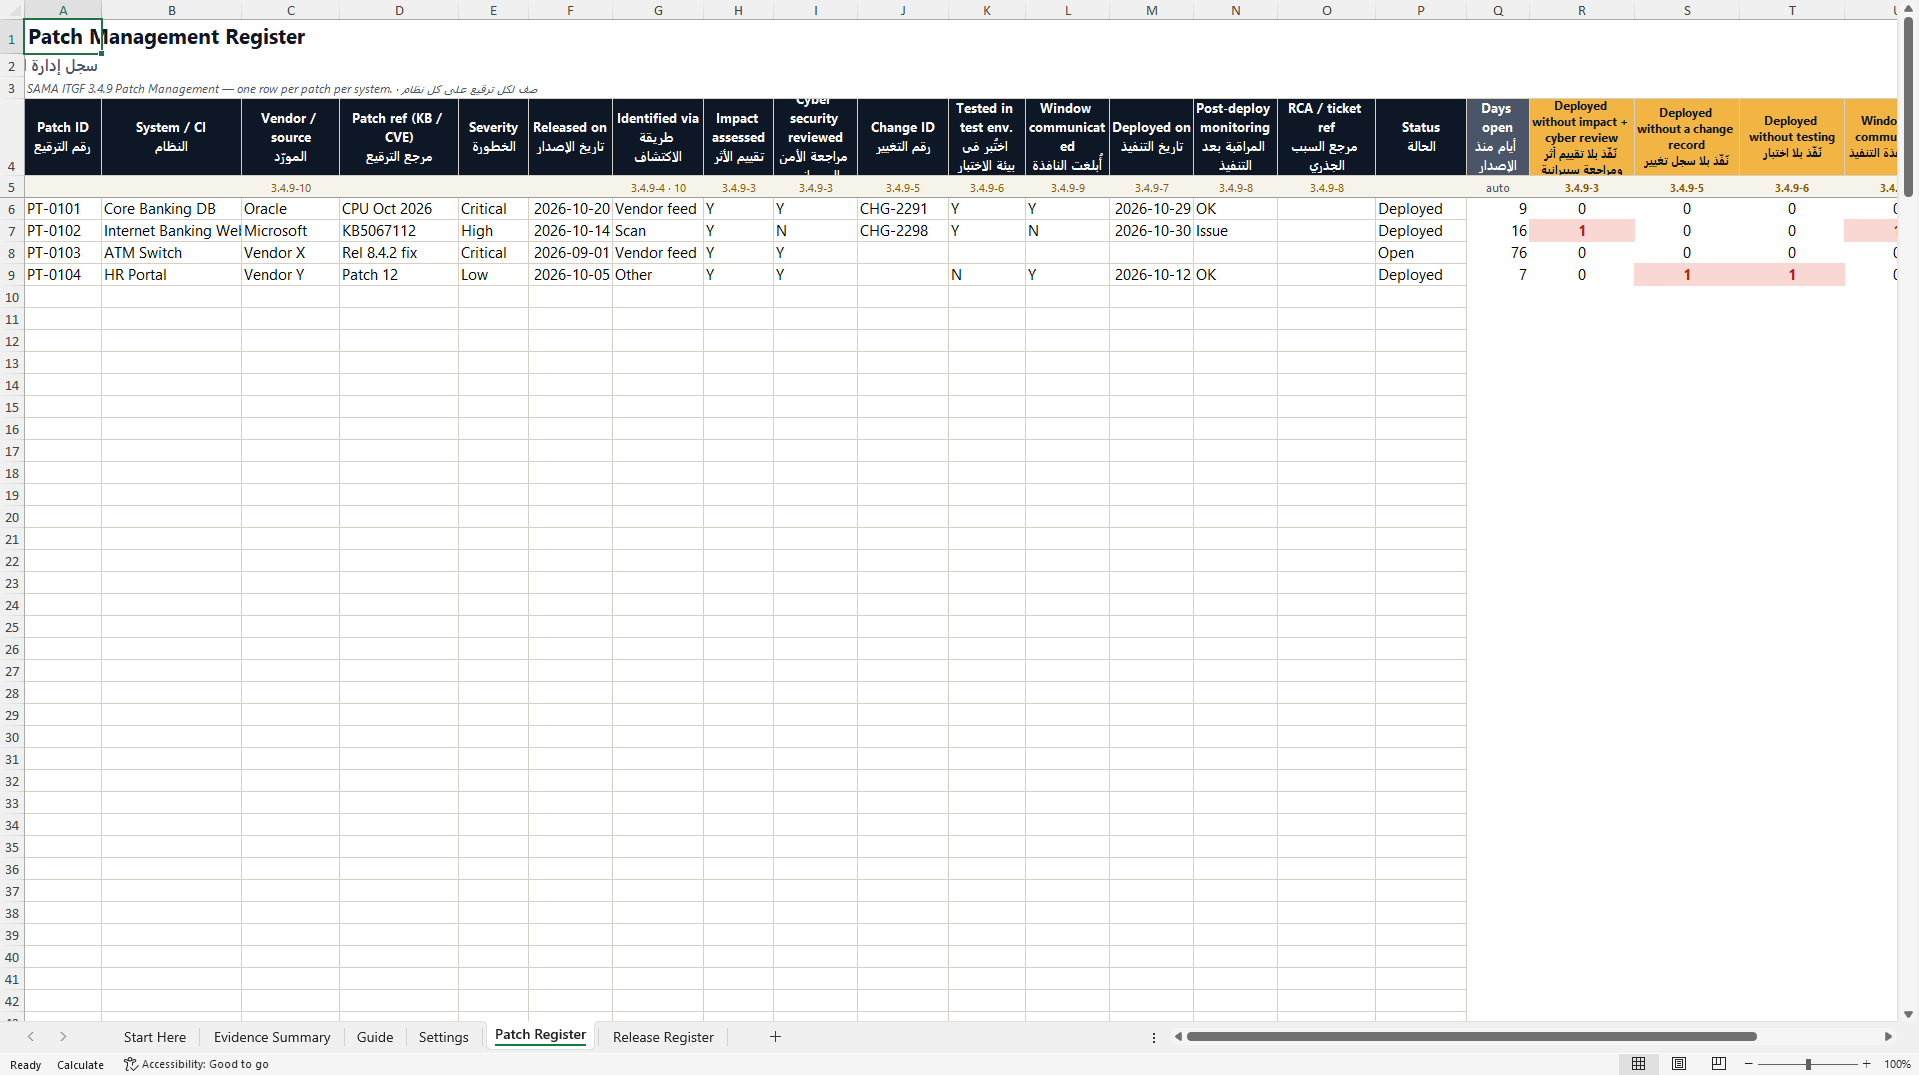
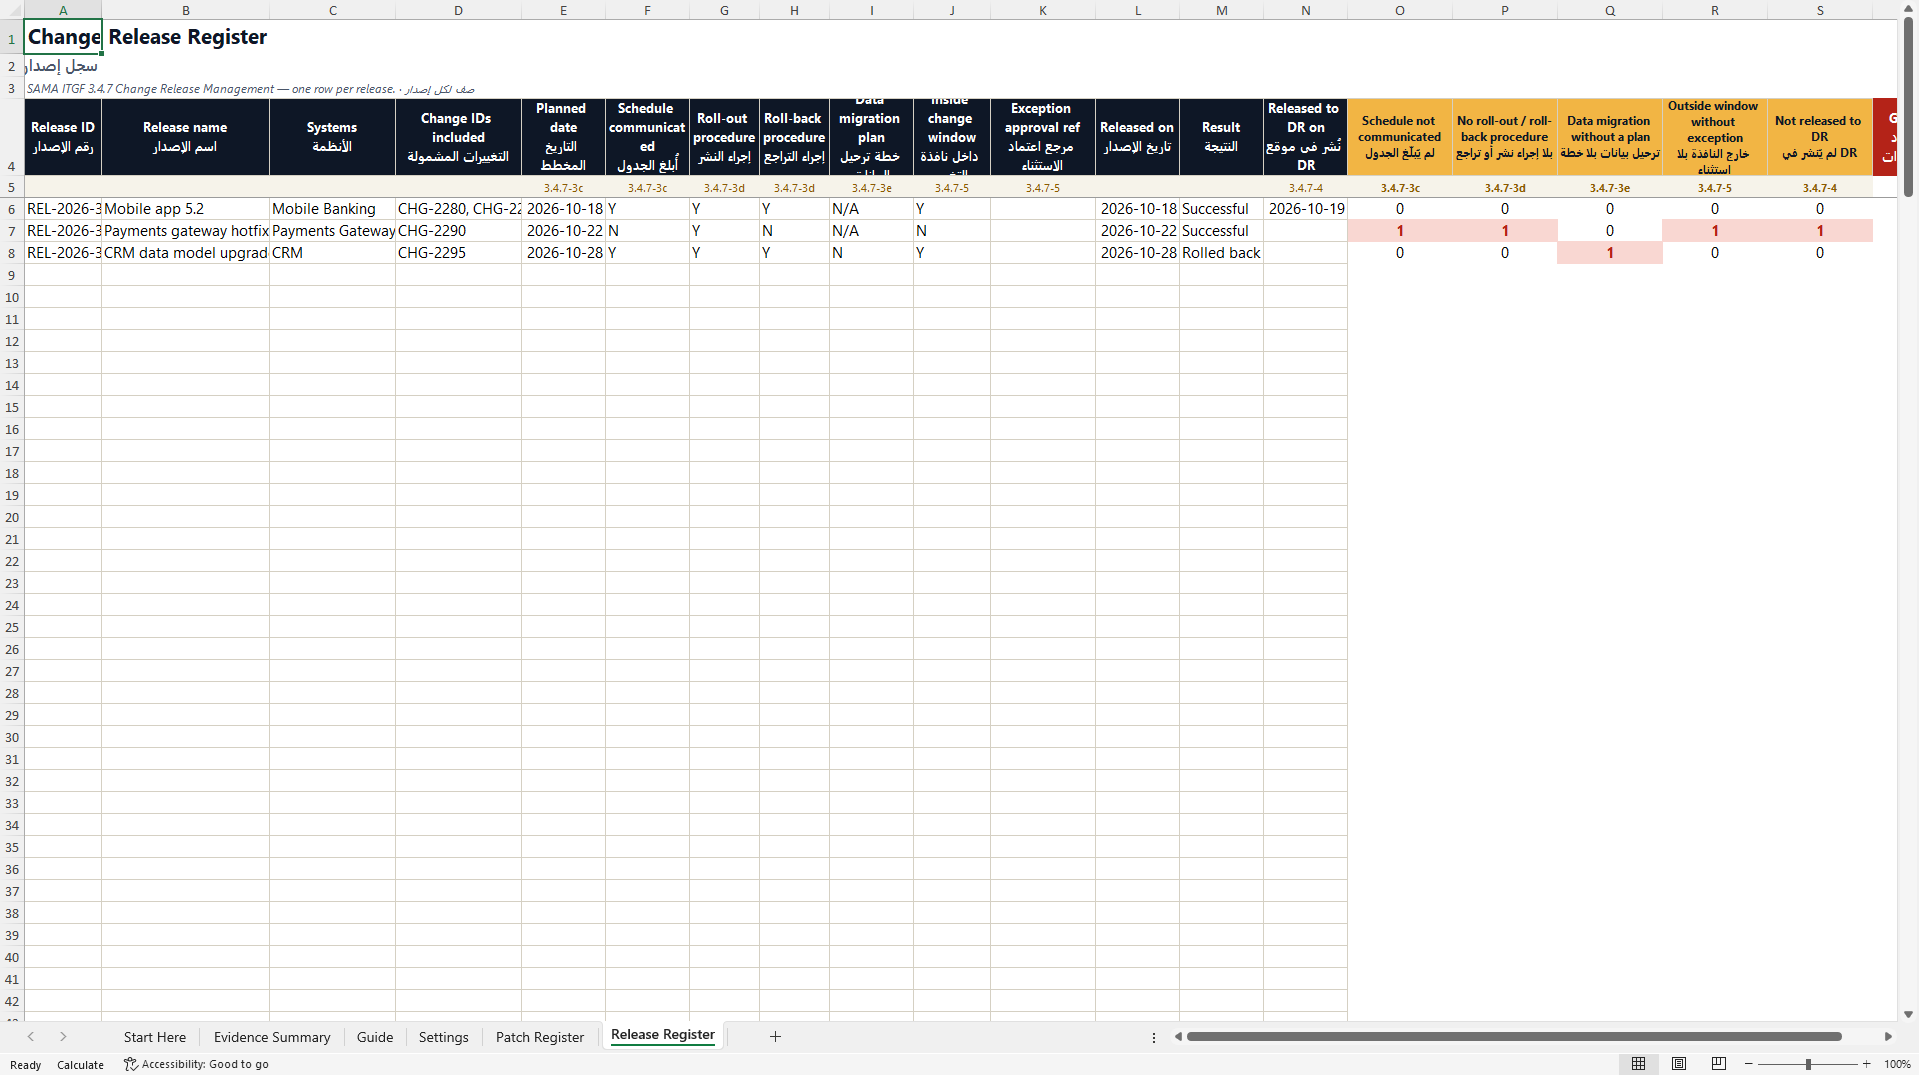
- Eleven automatic checks flag patches deployed without impact or cyber review, change record or testing, releases outside the change window without approval, and releases missing from DR.
- Patch age is calculated on every row and compared with YOUR target days for Critical, High, Medium and Low severity, set once in Settings.
- Release side covers schedule communication, roll-out and roll-back procedures, data migration plans, change-window exceptions and release to the DR site.
ARABIC EXCEL DESCRIPTION
Patch and release management is one of the first places an IT governance auditor looks, because the evidence is easy to request and hard to produce. For institutions supervised by the Saudi Central Bank, the questions follow the SAMA IT Governance Framework: was the patch assessed for impact and reviewed by cyber security, was it raised as a change, was it tested before production, was the deployment window communicated, was the system monitored afterwards, and how old is the patch compared with your own policy? For releases: was the schedule communicated, were roll-out and roll-back procedures in place, was there a data migration plan, did it happen inside the change window, and was it also released to the disaster recovery site?
This workbook records those answers and checks them automatically.
WHAT IS INSIDE
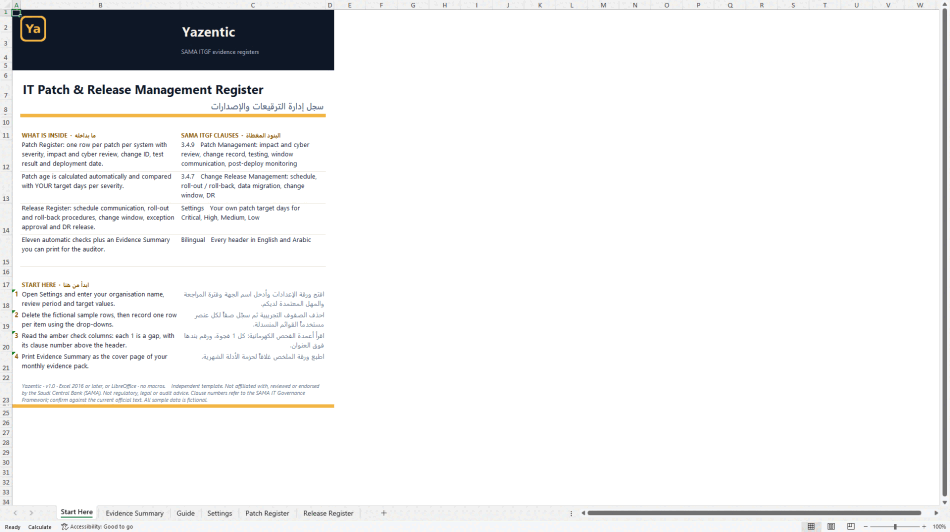
Patch Register (SAMA ITGF 3.4.9). One row per patch per system: patch ID, system, vendor, KB or CVE reference, severity, release date, how it was identified, impact assessed, cyber security reviewed, change ID, tested in a test environment, window communicated, deployment date, post-deployment monitoring, RCA reference and status. Days open is calculated for you.
Release Register (SAMA ITGF 3.4.7). Release ID, name, systems, change IDs included, planned date, schedule communicated, roll-out and roll-back procedures, data migration plan, inside the change window, exception approval reference, release date, result and DR release date.
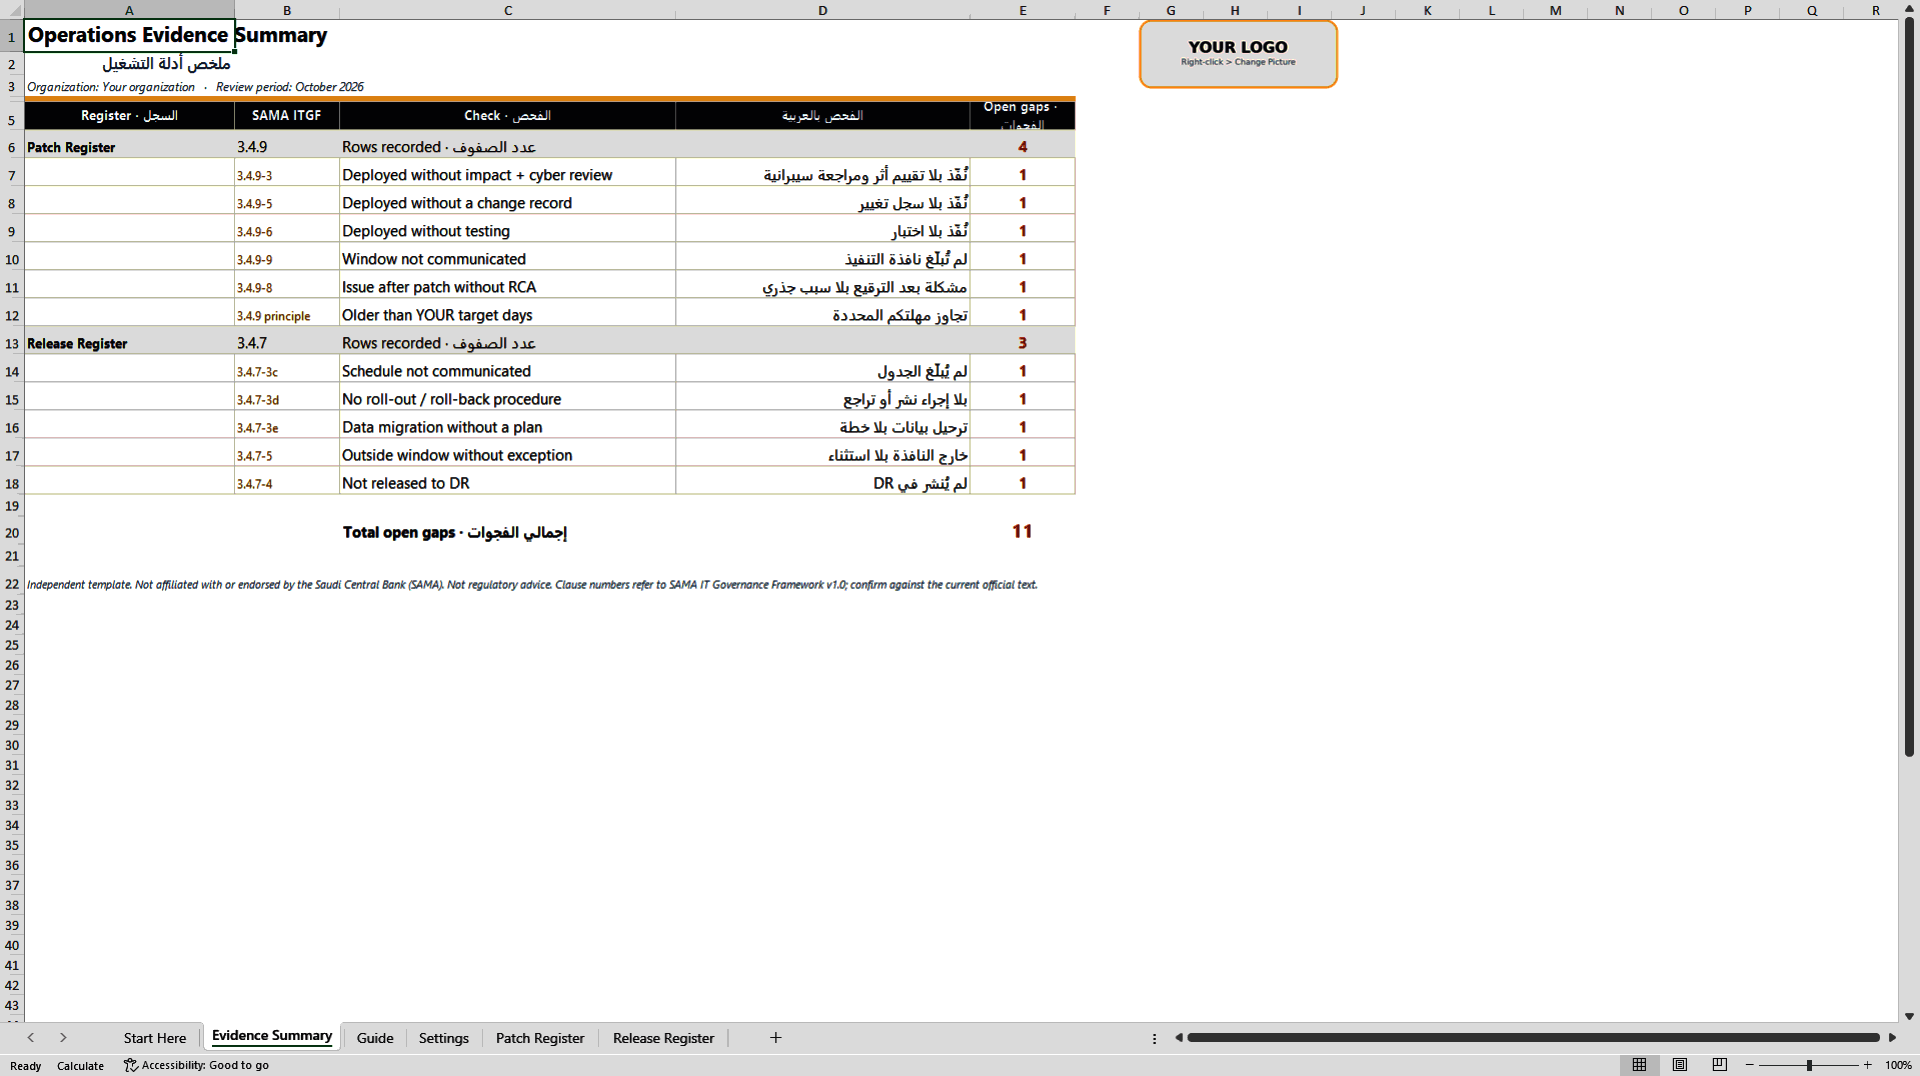
Eleven automatic checks. Six on patches: deployed without impact and cyber review, without a change record, without testing, without a communicated window, issue after deployment without RCA, and older than your target days for its severity, while patches marked Not applicable stay silent. Five on releases: schedule not communicated, no roll-out or roll-back procedure, data migration without a plan, outside the window without an exception, and a successful release not yet deployed to DR.
Evidence Summary. Rows and open gaps per check with a grand total, ready to print as the cover of your monthly evidence pack.
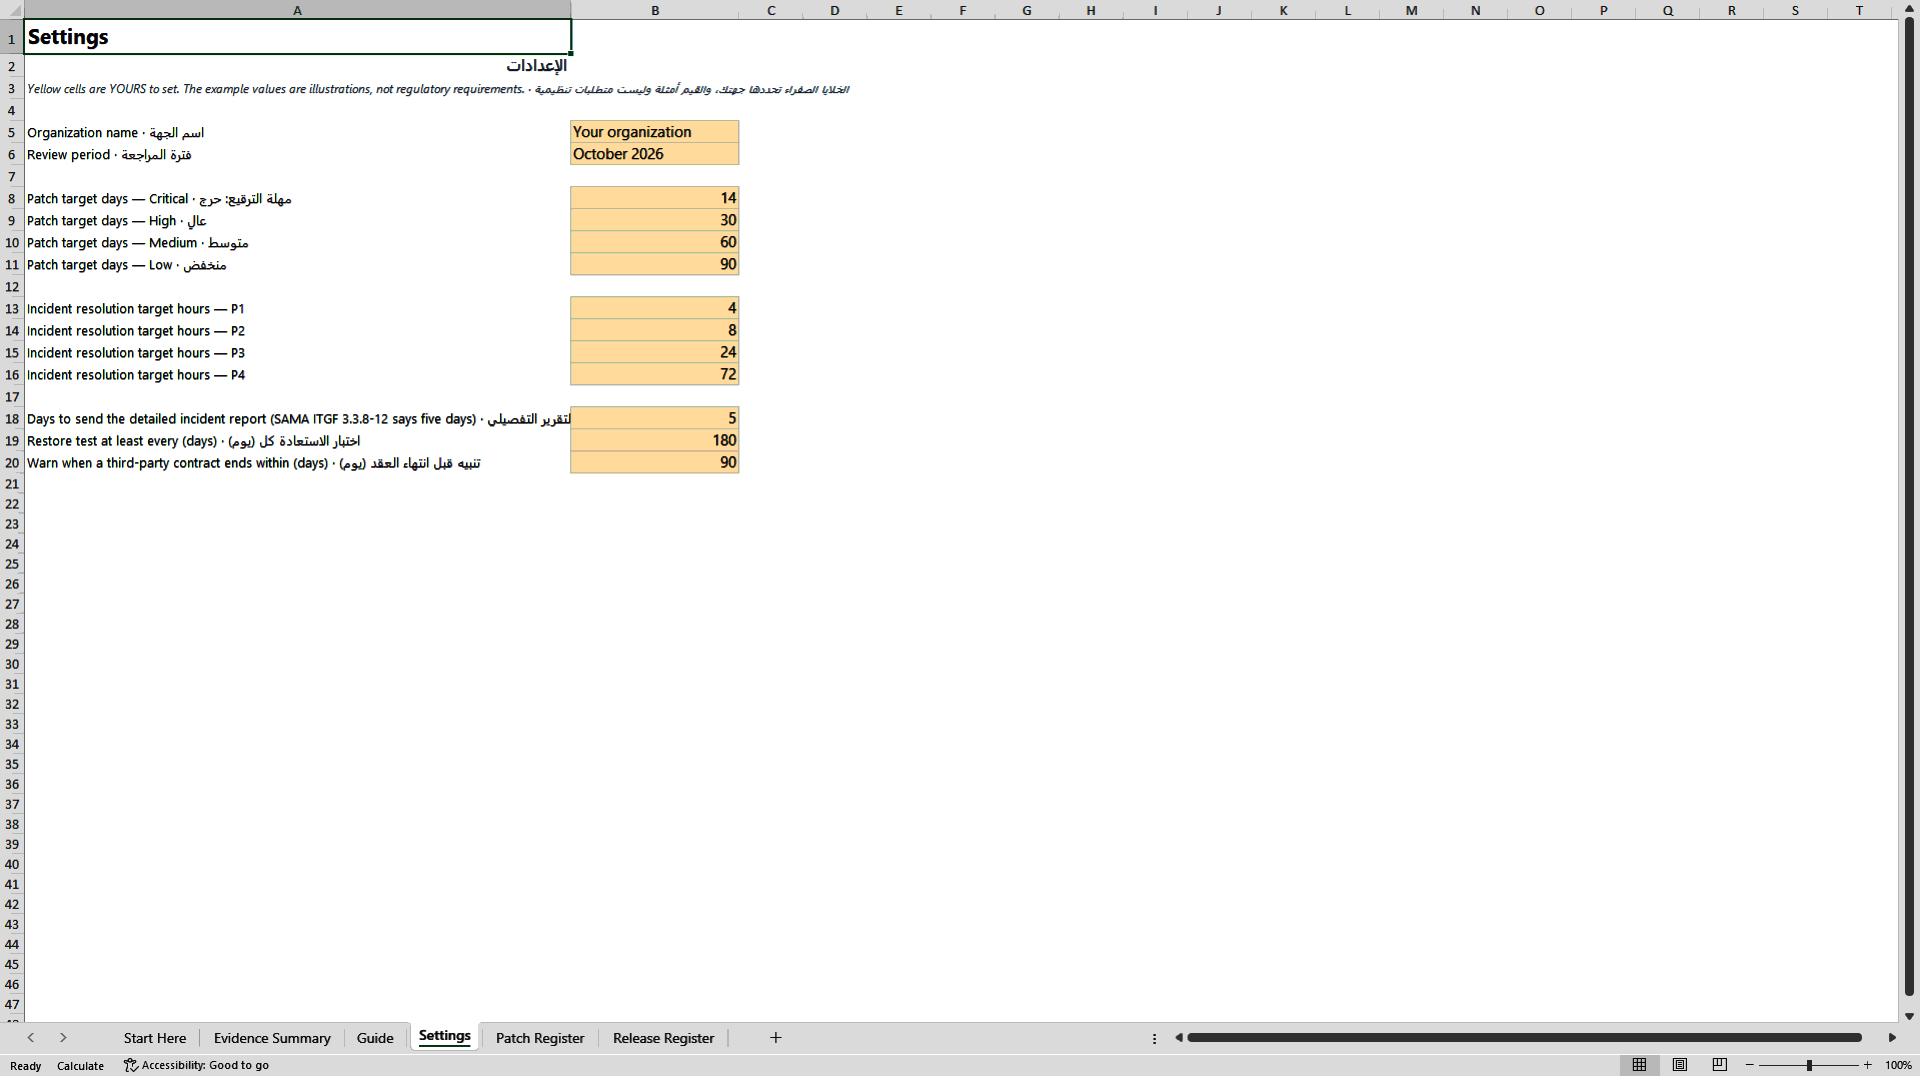
Settings. Your organisation, review period and patch target days per severity. The examples are illustrations, not SAMA requirements.
WHY IT IS DIFFERENT
Built by a practitioner with more than ten years in enterprise IT operations and change governance inside a Saudi telecom group. Bilingual English and Arabic headers, clause numbers above every column, drop-downs on every field that feeds a check, and room for 200 rows per register.
COMPATIBILITY
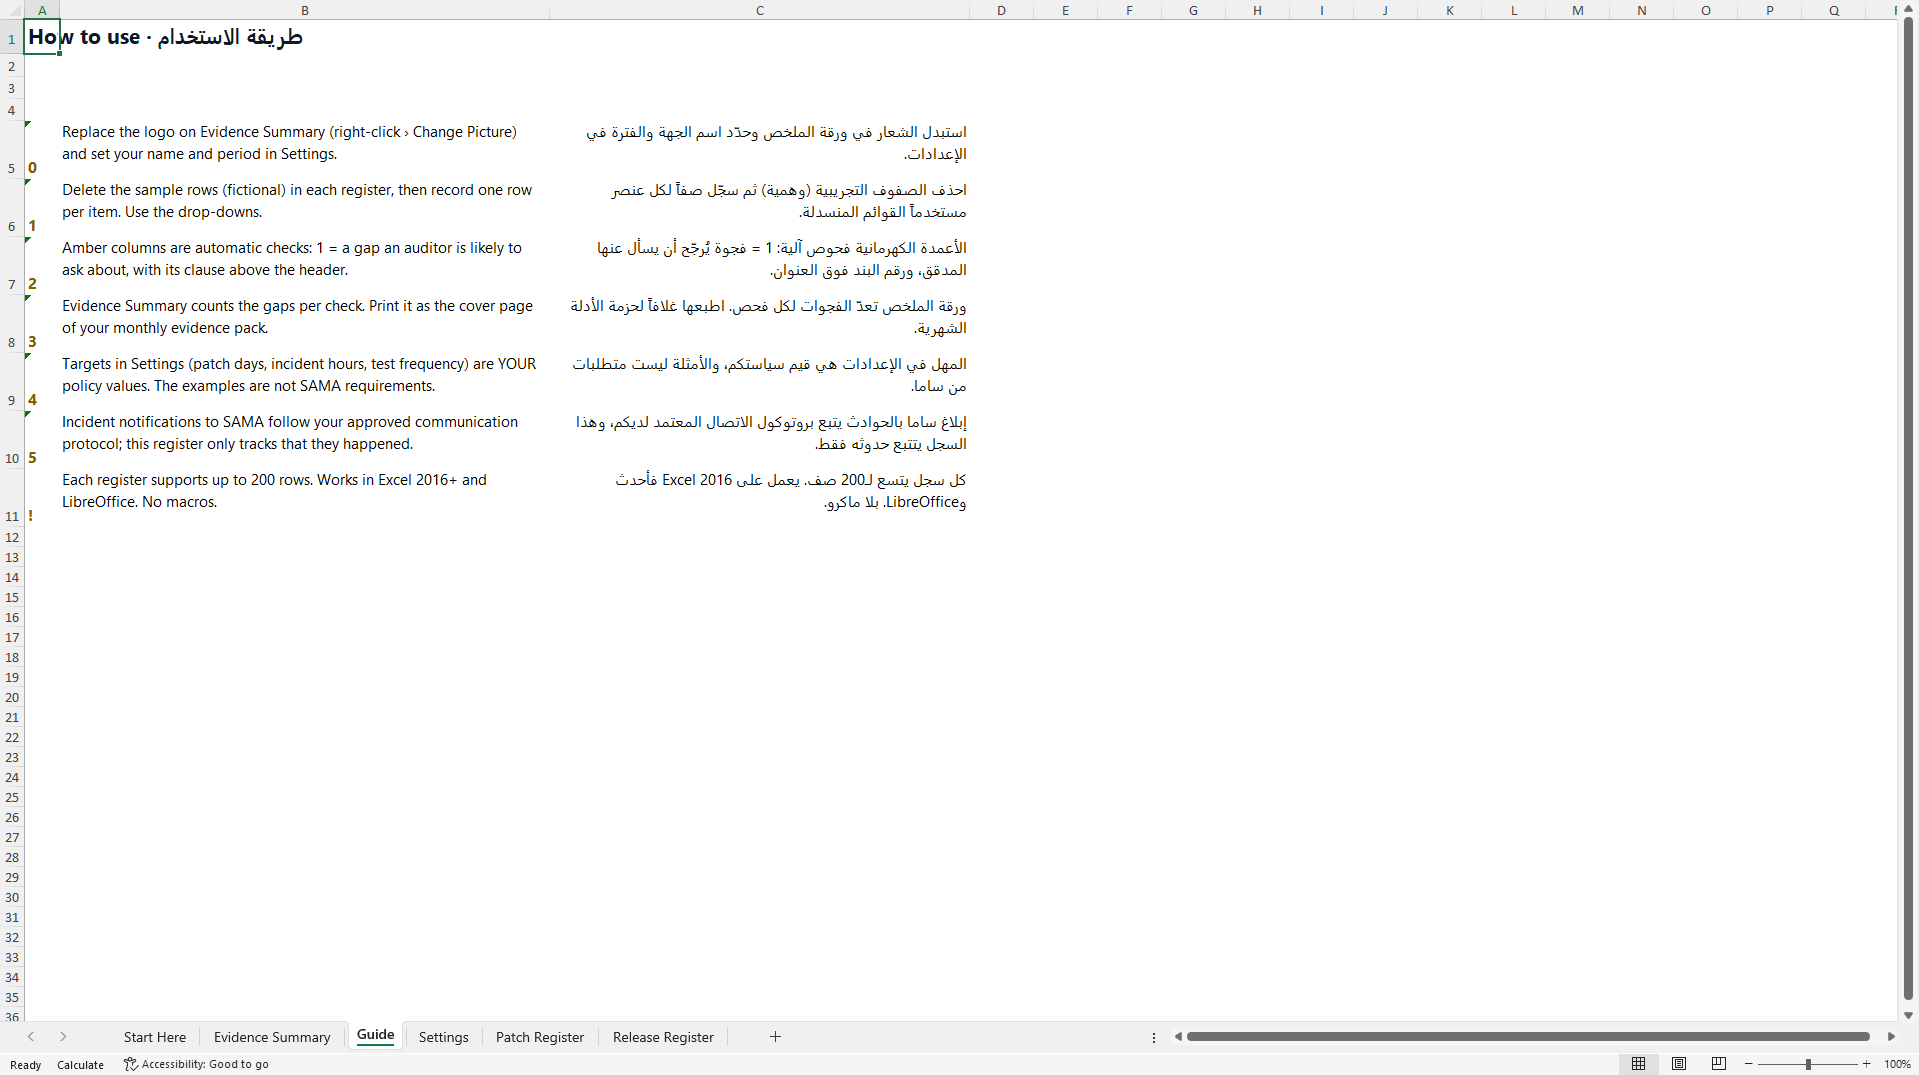
Excel 2016 or later, or LibreOffice. No macros. Fictional sample rows show every check firing before you replace them with your own data.
Independent template. Not affiliated with, reviewed or endorsed by the Saudi Central Bank (SAMA). Not regulatory, legal or audit advice. Confirm clause numbers against the current official text.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Arabic, ITSM, IT Governance Excel: SAMA ITGF Patch & Release Management Register Excel (XLSX) Spreadsheet, Elsadig Hamedelniel




























