 Click main image to view in full screen. Unlock all 9 preview images:
SAMA IT Governance Change and Operations Evidence Kit – Excel XLSX
Excel (XLSX) + Zip archive file (ZIP) Arabic


BENEFITS OF THIS DOWNLOADABLE EXCEL DOCUMENT
- Ten clause-referenced registers covering change, CAB, patch, release, incident, problem, backup restore tests and third-party SLA review.
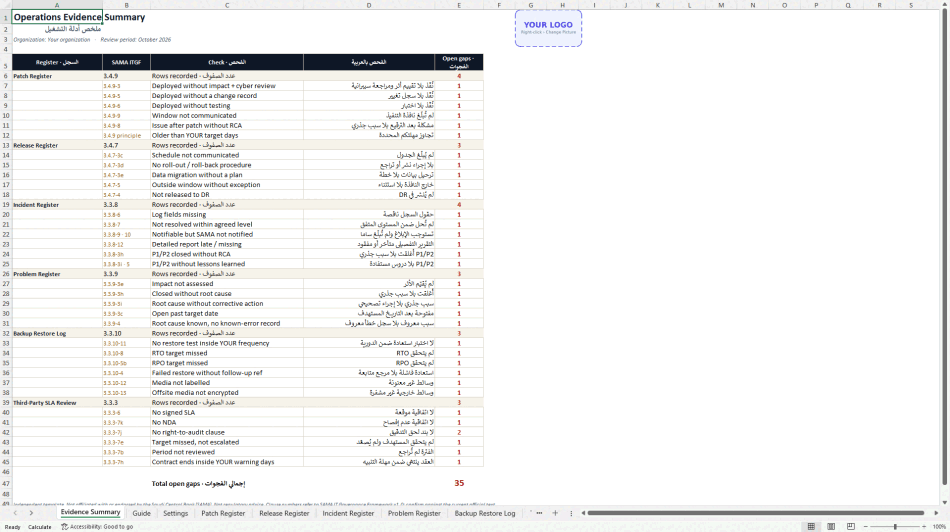
- 34 automatic checks that count your evidence gaps and name the SAMA ITGF clause each gap comes from.
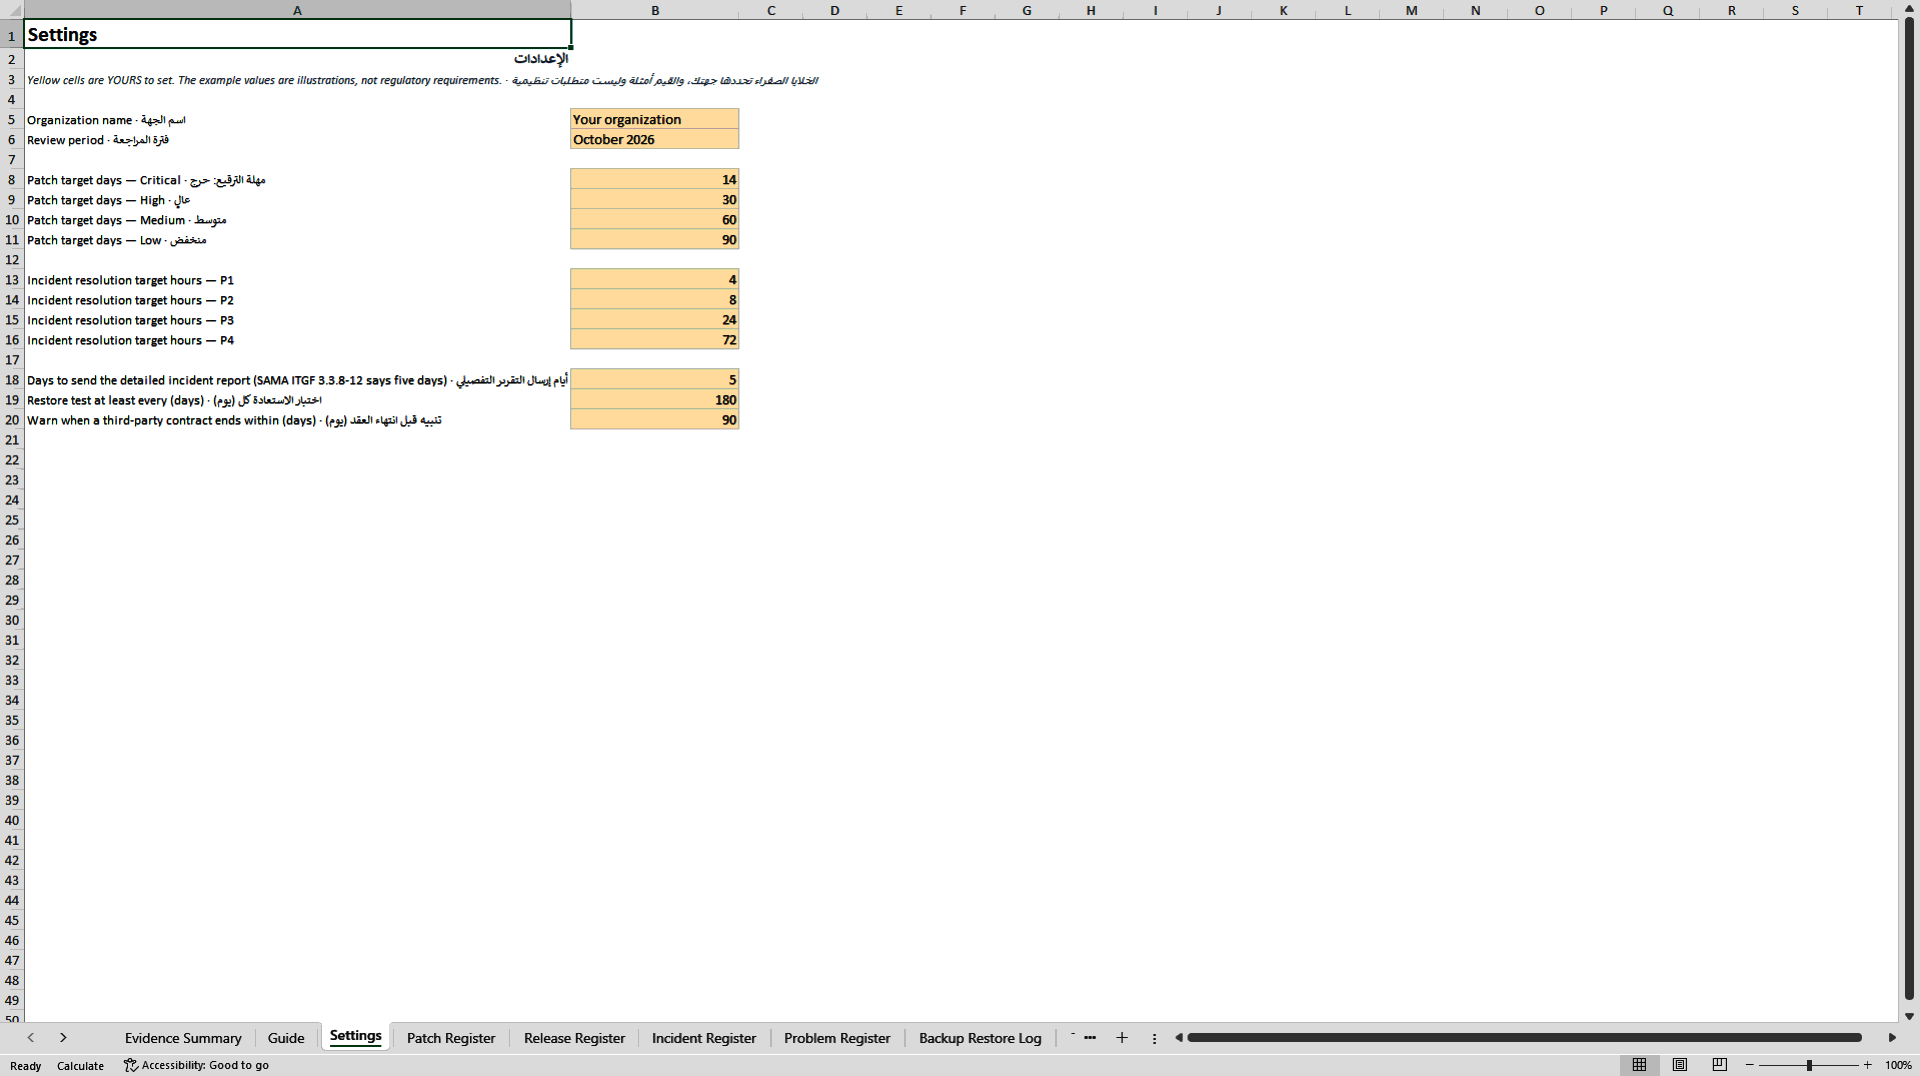
- Settings sheets so every check measures against your own approved policy targets, plus a bilingual guide mapping auditor questions to records.
COMPLIANCE EXCEL DESCRIPTION
This is a template kit, not a consulting report. It gives IT operations, change and service-management teams at SAMA-regulated organisations a ready structure for the evidence an IT governance audit usually asks for, organised by the clauses of the SAMA IT Governance Framework (sections 3.3 and 3.4).
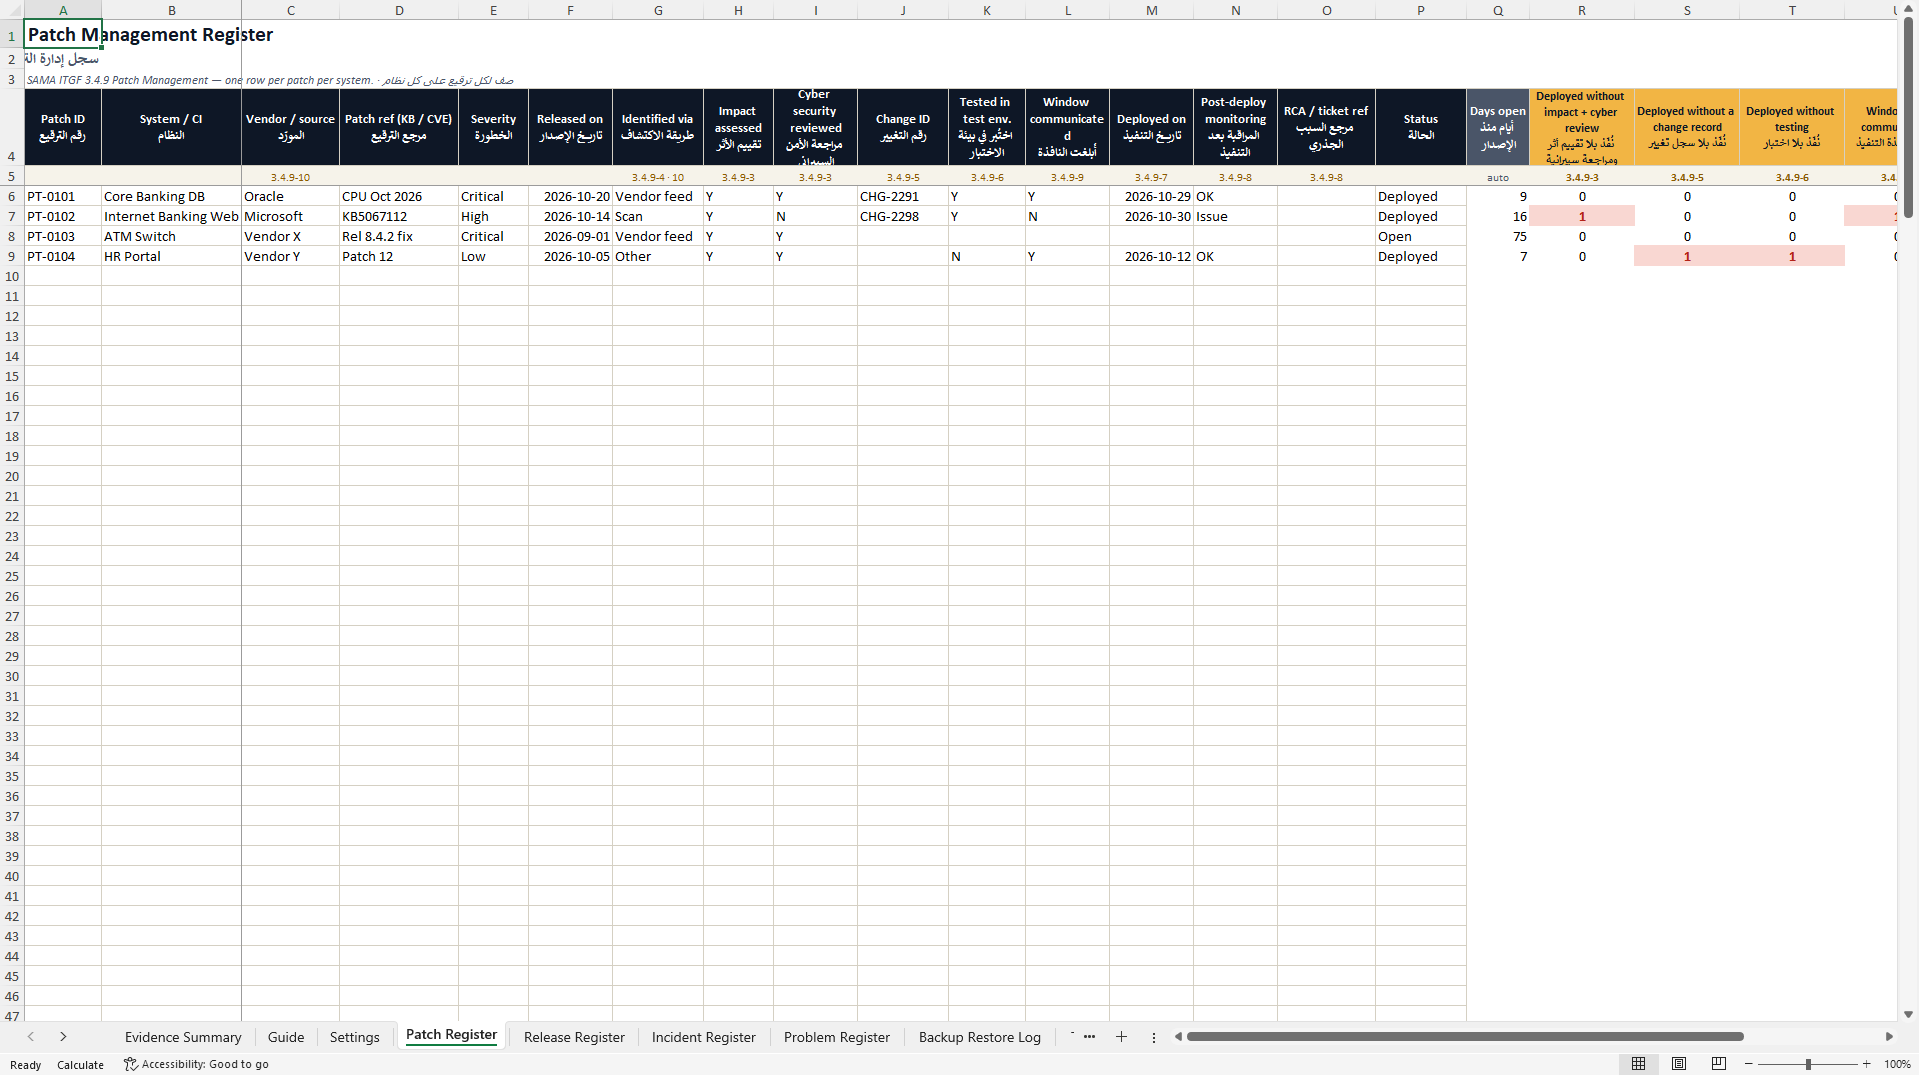
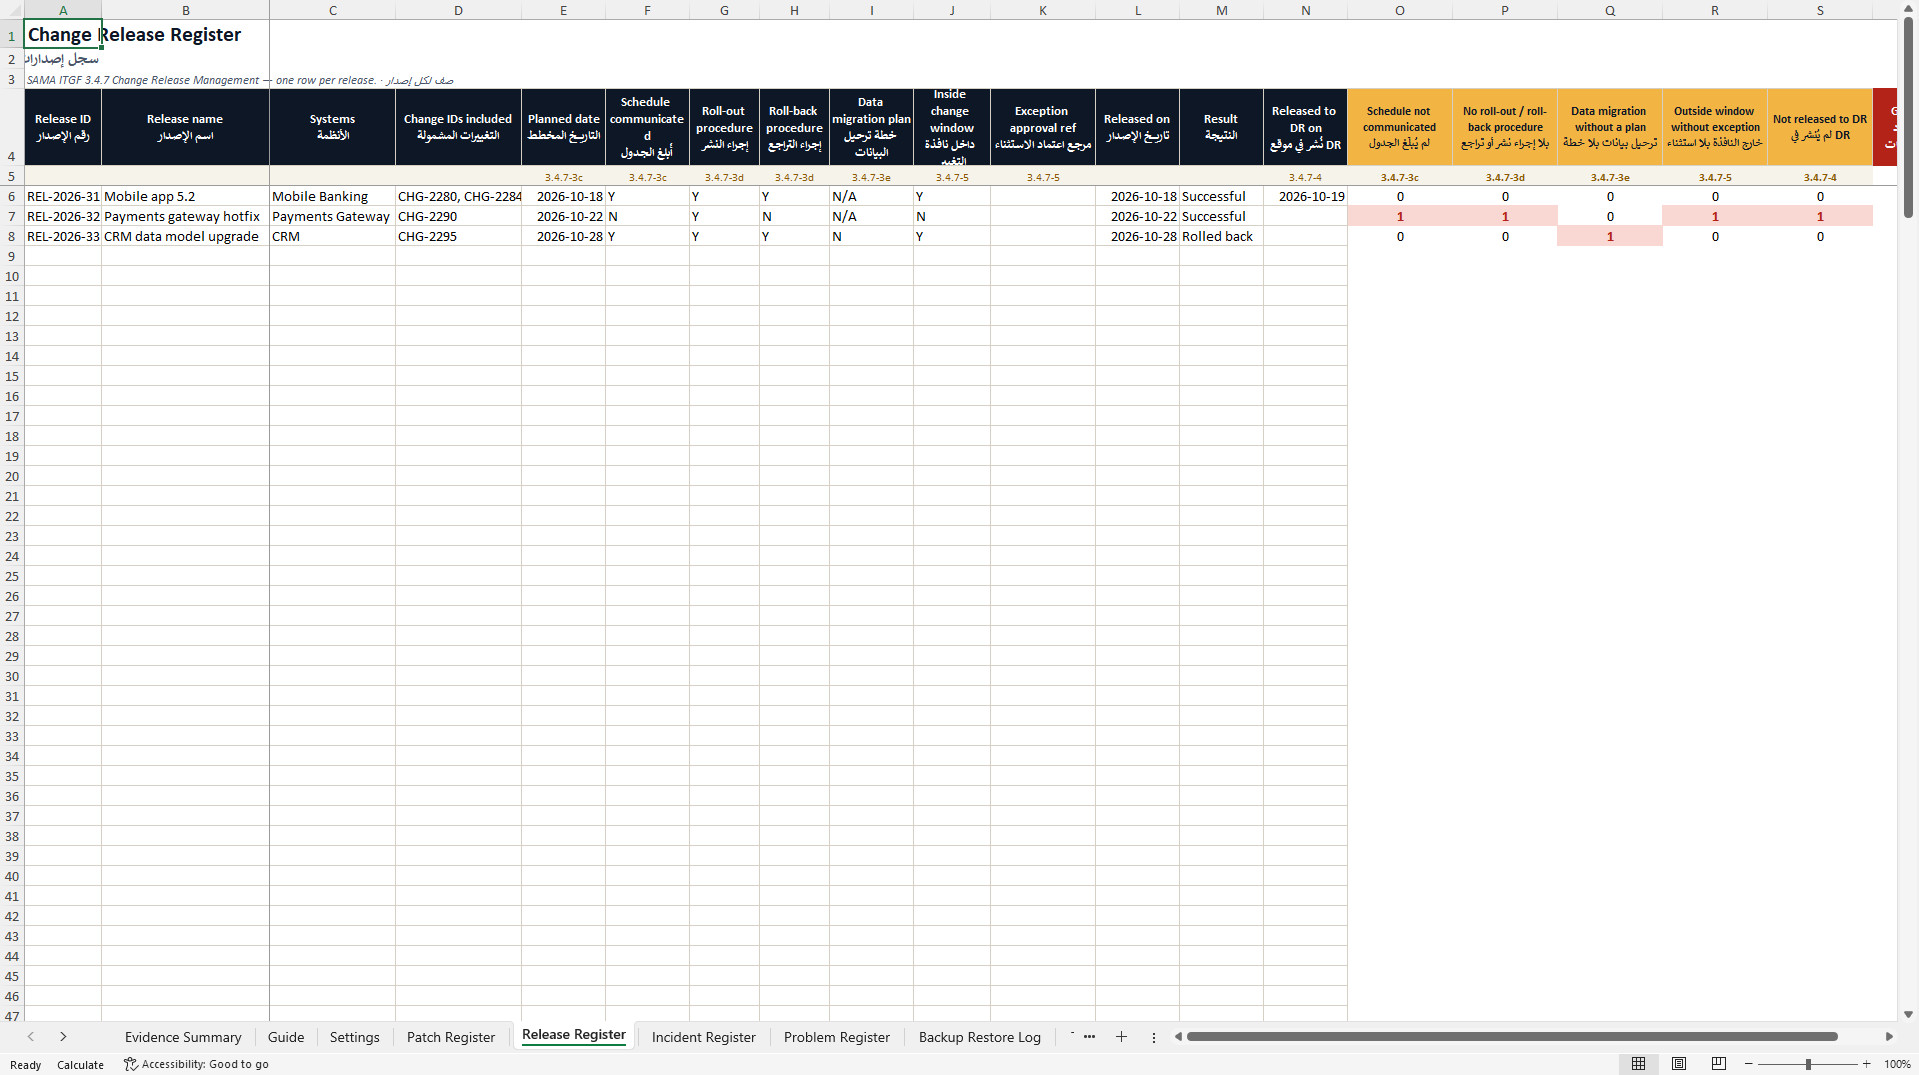
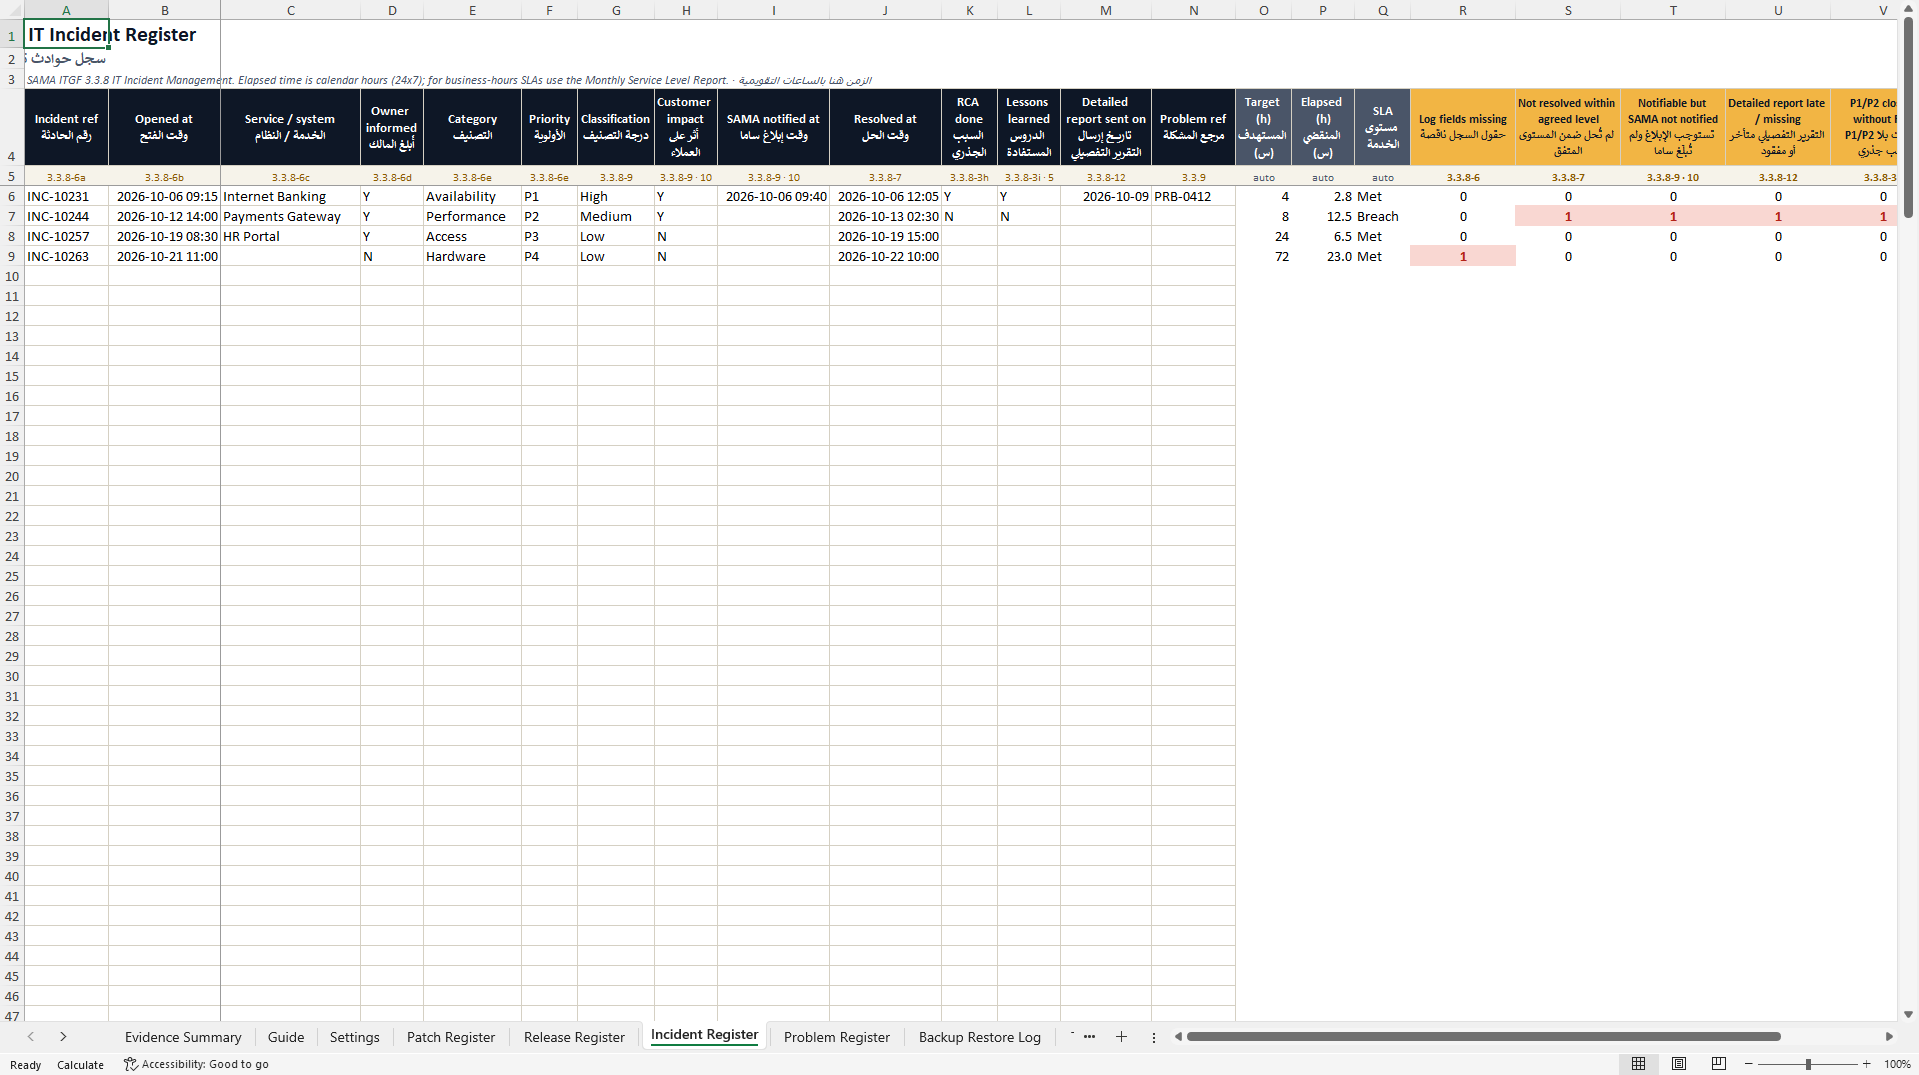
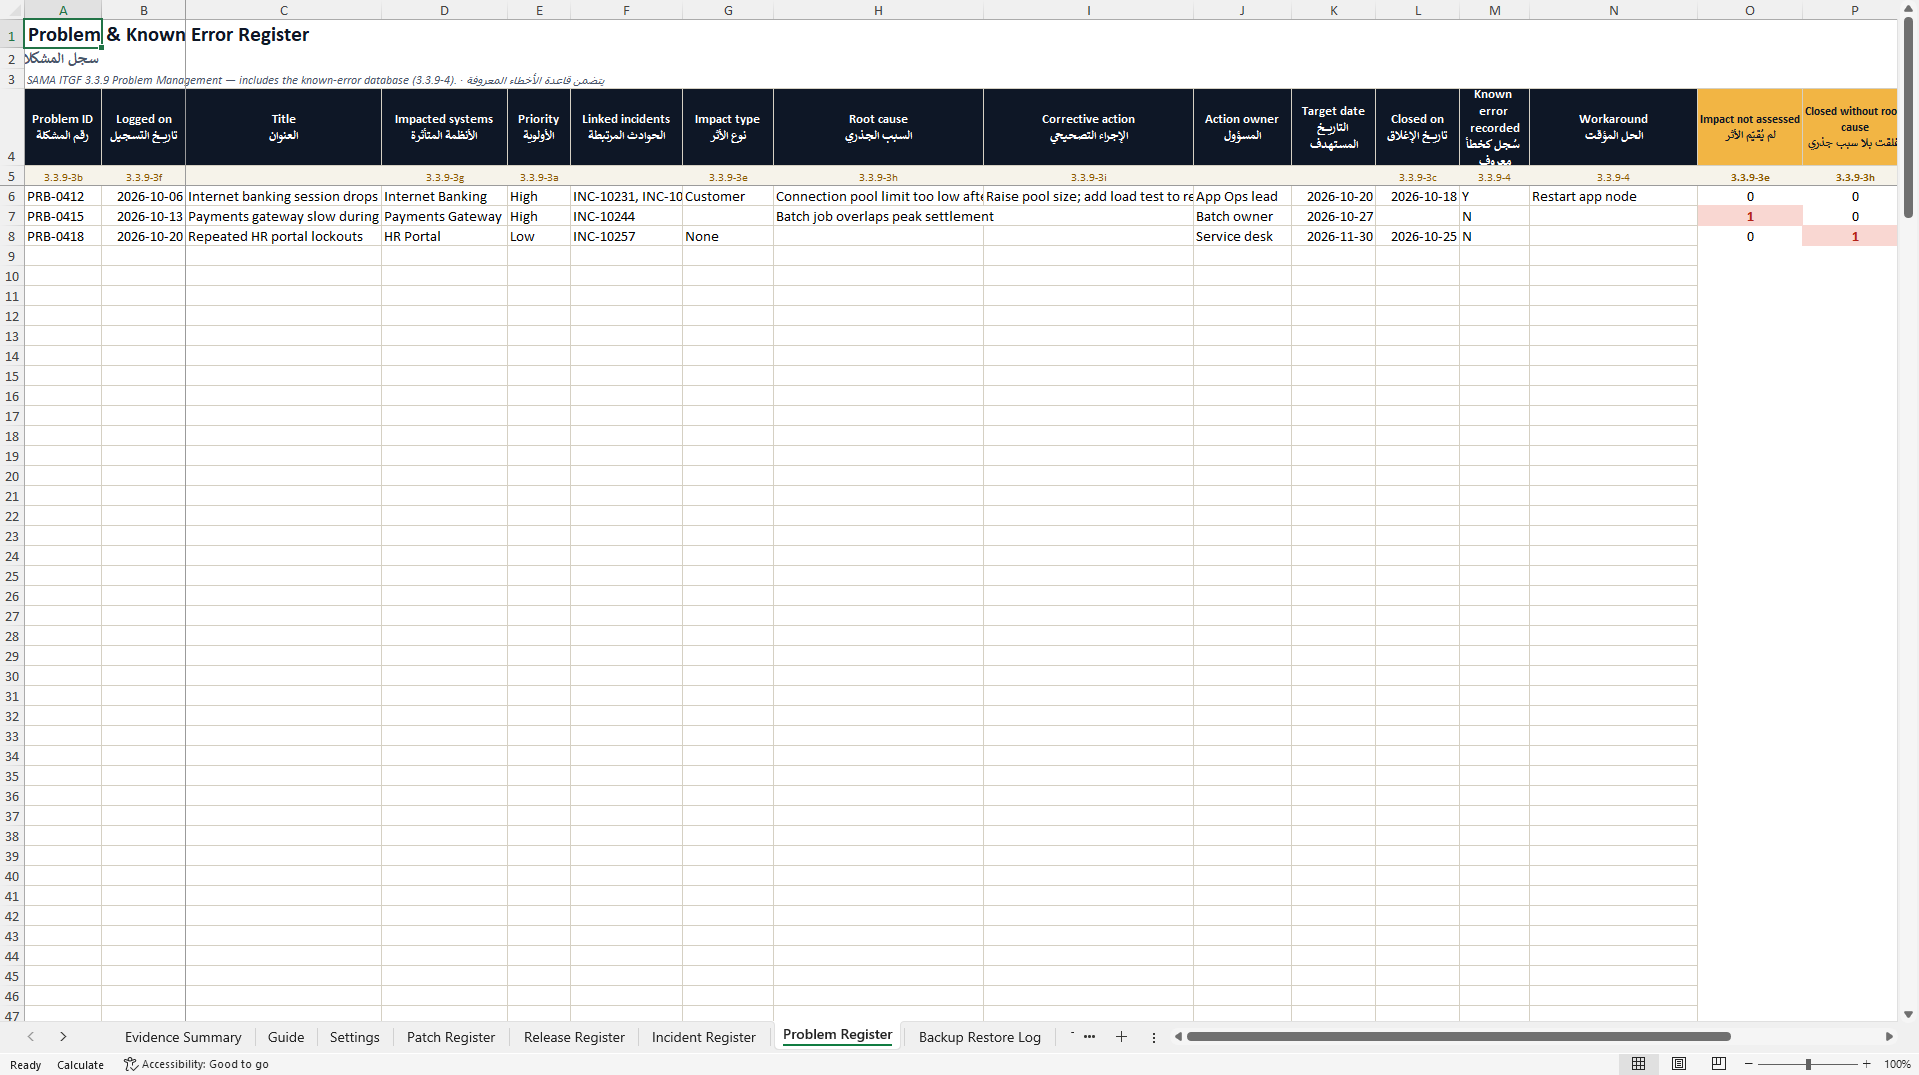
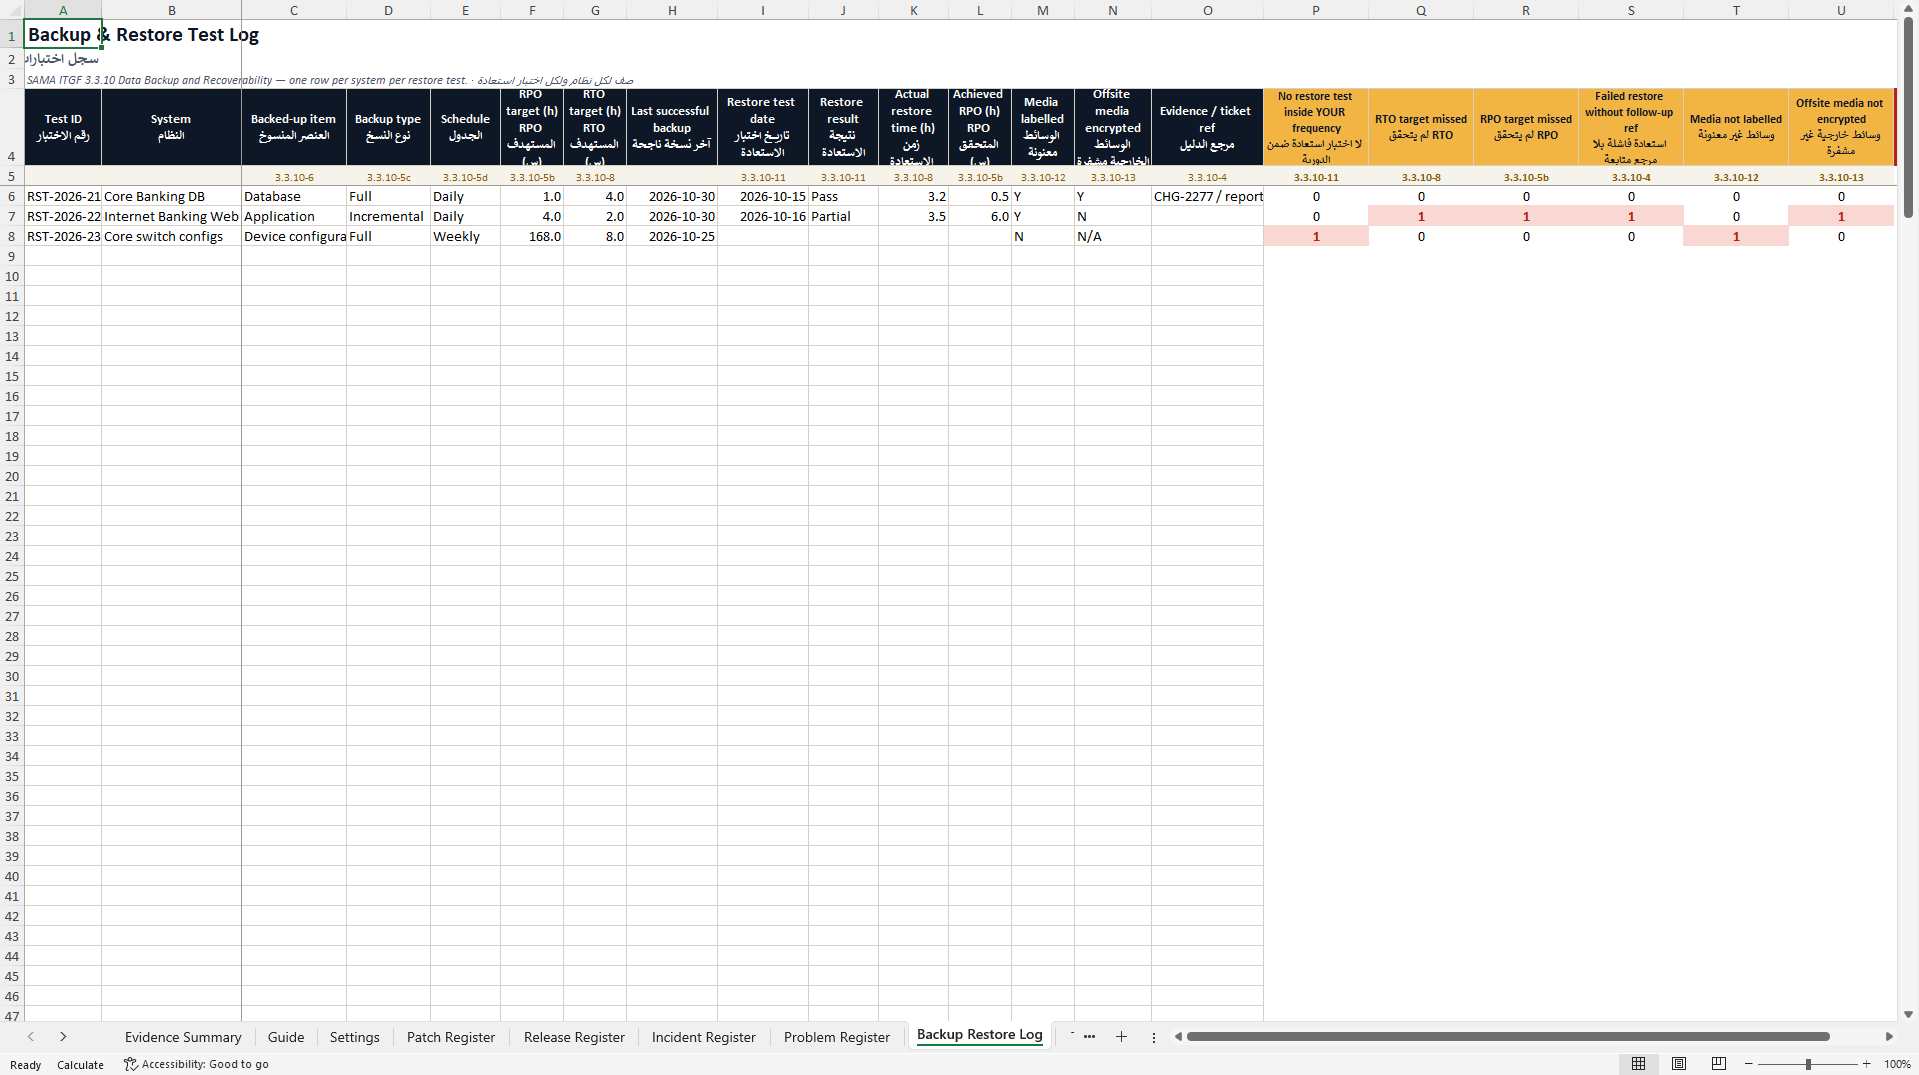
The primary document is the Operations Evidence Registers workbook. It holds six registers, each column tied to its clause number: Patch Management (3.4.9), Release Management (3.4.7), Incident Management (3.3.8), Problem and Known Error (3.3.9), Backup and Restore Test Log (3.3.10) and Third-Party SLA Review (3.3.3), plus an Evidence Summary page that counts your gaps. The workbook runs 34 automatic checks – a patch deployed with no cyber security review, a restore test overdue against your own policy interval, an incident resolved past its target, a problem with no root cause recorded, an emergency change with no post-implementation review, a third-party SLA with no documented periodic review – and each check carries the clause number it comes from. Target values such as patch days by severity, incident response hours by priority and restore-test frequency are set once on a Settings sheet, so the checks measure against your approved policy values rather than ours.
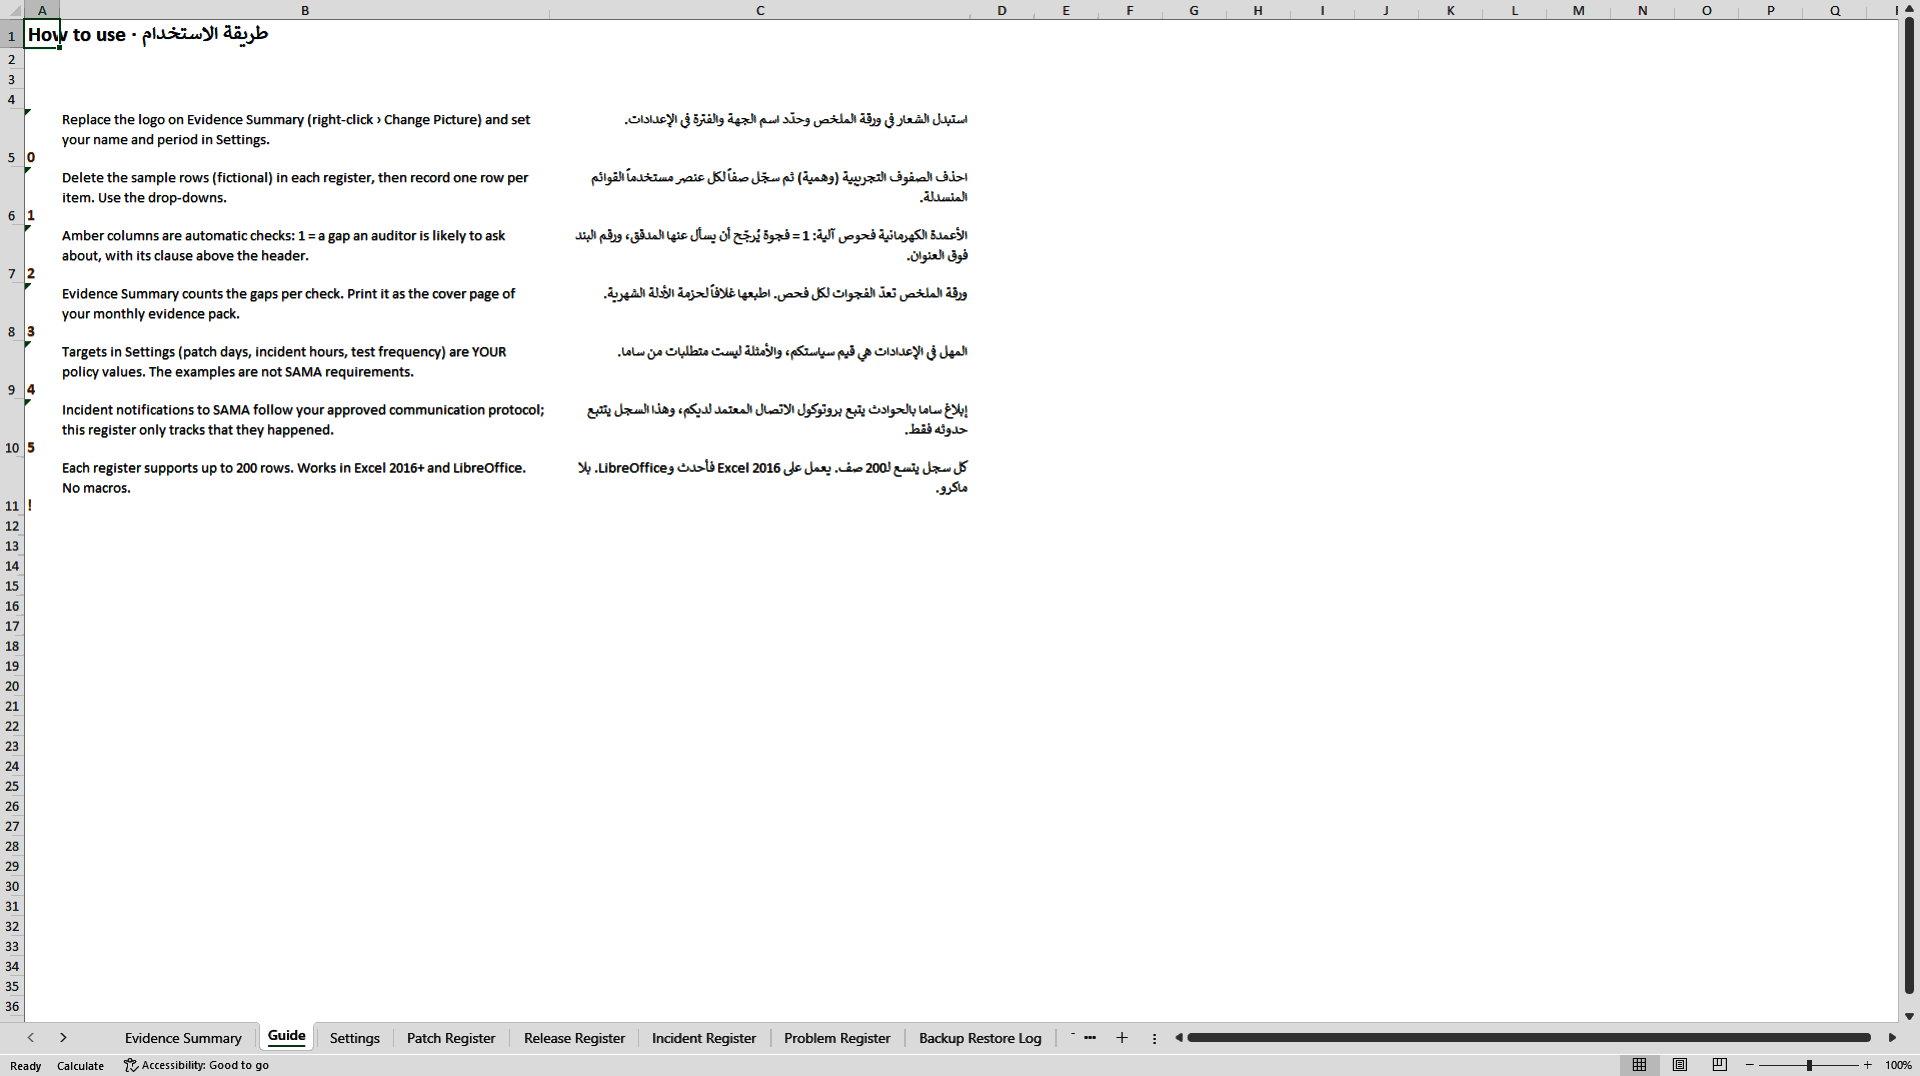
The supporting file adds three more documents. A two-page Start Here guide in English and Arabic maps each auditor question to the register that answers it. A Change and CAB Register workbook covers the change log, CAB minutes, emergency CAB decisions, emergency post-implementation reviews, an Audit Readiness page and a clause map. A Monthly Service Level Report is built for the Sunday-to-Thursday Gulf working week with a holiday calendar and business-hours clock. In total the kit holds ten registers and three one-page summary reports.
How it works: paste your records from your ITSM tool into each register and fill the Y/N evidence columns from the tickets. The check columns flag gaps row by row, and the summary pages show how many items would fail an evidence request today. Fictional sample rows are included so you can watch every check fire before you delete them. All logic uses standard spreadsheet formulas (IF, AND, OR, SUM, COUNTA, TODAY) and there are no macros. Recalculation was verified in LibreOffice Calc.
Who it is for: IT service managers, change managers, CAB chairs, IT risk and internal audit teams at banks, insurers, finance companies, payment providers and fintechs in Saudi Arabia, and the managed-service providers and consultancies that serve them.
What it is not: this is not legal, regulatory or audit advice, and it does not replace the official framework text. The clause summaries are the author's own wording, not the official text. Always confirm against the current official version on the SAMA Rulebook before an audit. All sample data is fictional. This is an independent template, not affiliated with or endorsed by the Saudi Central Bank.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Compliance, Arabic, IT Governance Excel: SAMA IT Governance Change and Operations Evidence Kit Excel (XLSX) Spreadsheet, Elsadig Hamedelniel




























