 Click main image to view in full screen.
IT Security Policy Pack for Small Businesses (EU) – Word DOCX
Word (DOCX) + Zip archive file (ZIP) 4 Pages


BENEFITS OF THIS DOWNLOADABLE WORD DOCUMENT
- Give staff clear IT and security rules in plain English that explain why each rule matters, with a lighter or stricter option where firms differ.
- Turn every policy rule into one of 37 tracked measures with an owner, a due date and evidence, plus a calendar for recurring checks.
- Answer customer security questionnaires faster, because each policy maps to the GDPR, NIS2 art. 21(2), ISO/IEC 27001:2022 Annex A and the ENISA SME guide.
CYBER SECURITY WORD DESCRIPTION
Most policy templates tell staff what to do but not why, and stop at the document. This pack gives a small EU organisation (about 2 to 50 staff) the core IT and security policies in plain English, explains each important rule, offers a lighter and a stricter option where firms differ, and links every rule to a tracker with owners, due dates and evidence. A4, editable in Word and Excel.
What you get (11 files plus an AI-assistant bonus):
1. Acceptable use policy (Word): accounts, devices, software, payment-fraud checks, three simple information labels, generative AI tools, monitoring that respects staff privacy, reporting mistakes.
2. Passwords, MFA and access policy (Word): password rules in line with current European guidance (long, unique, no forced 90-day changes), where MFA is required, admin accounts, access reviews.
3. Remote work and own devices policy (Word): three models to choose from, minimum device rules, what the employer can and cannot see or wipe on a personal phone.
4. Backup and recovery policy (Word): a fill-in table per system (frequency, retention, RPO/RTO), 3-2-1 plus one copy out of ransomware's reach, cloud services, restore tests.
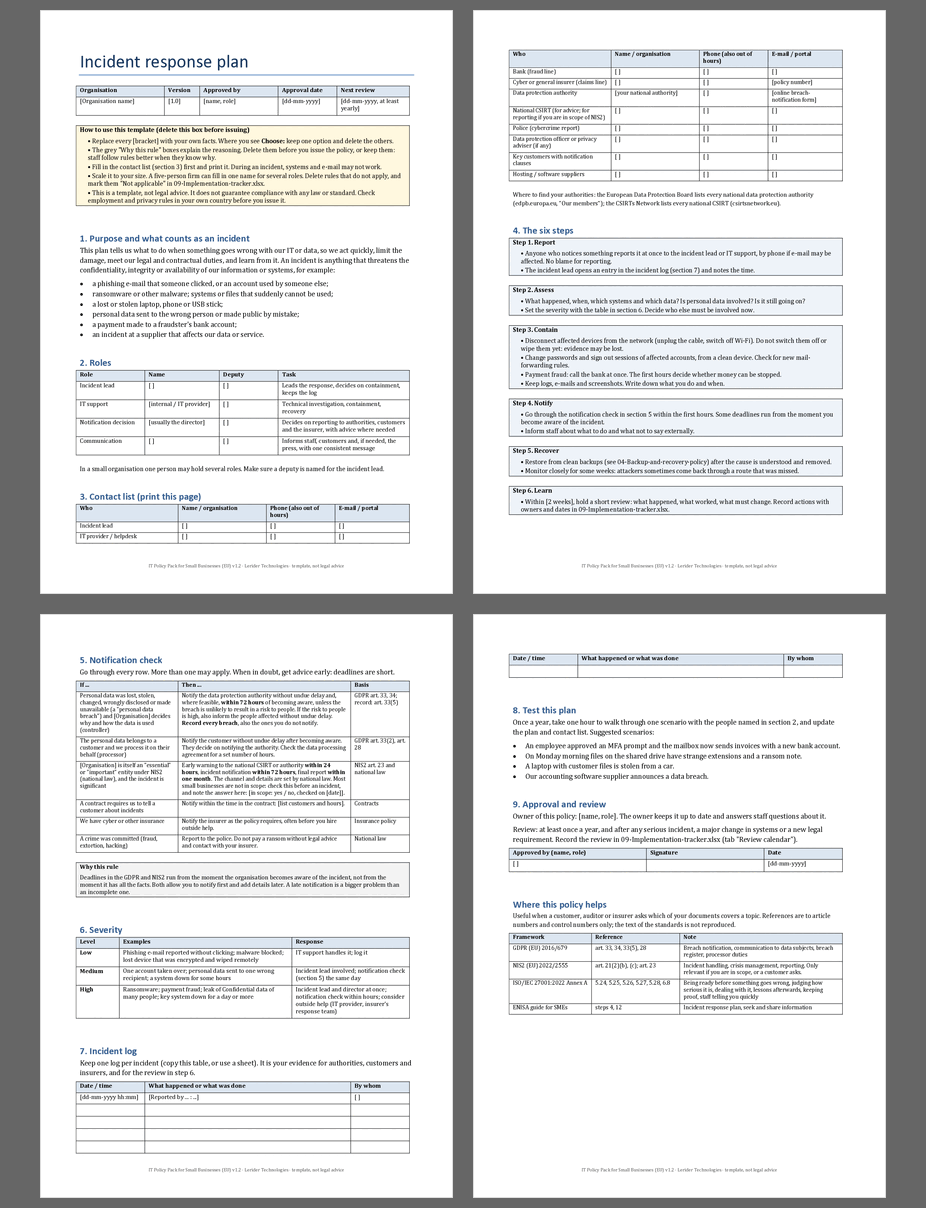
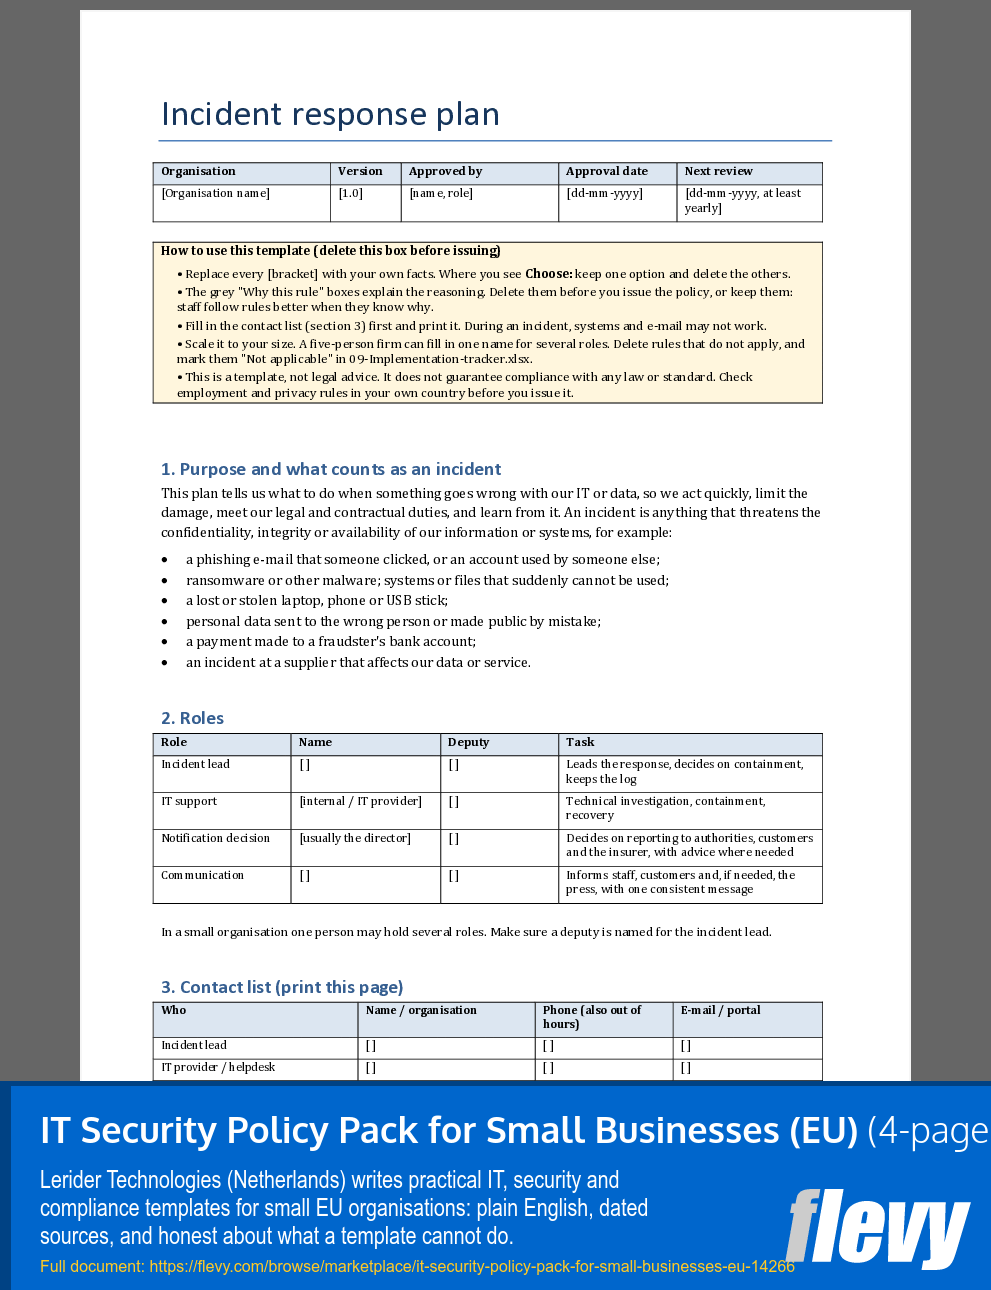
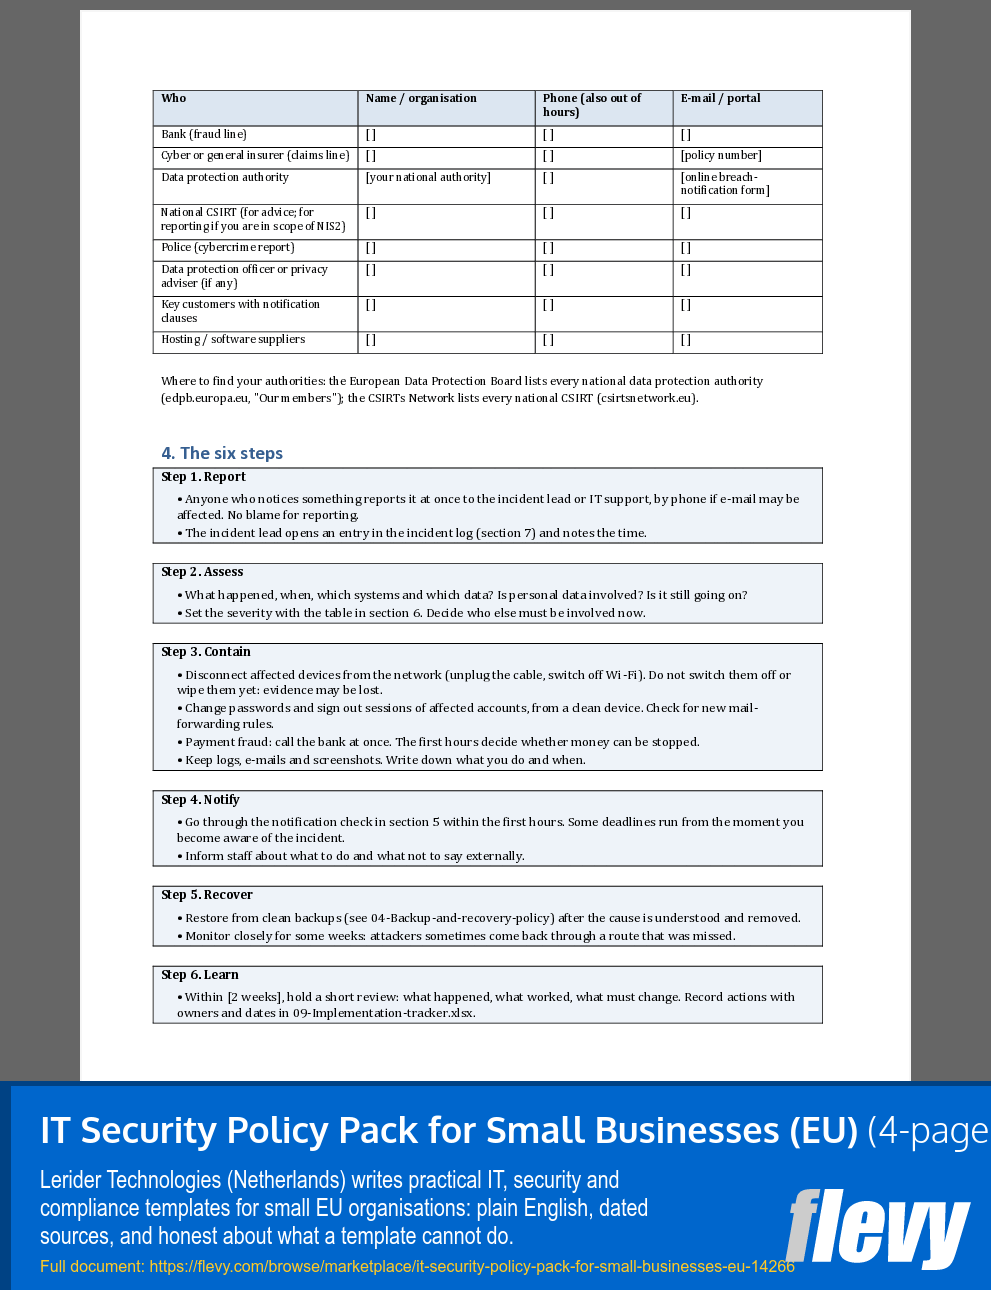
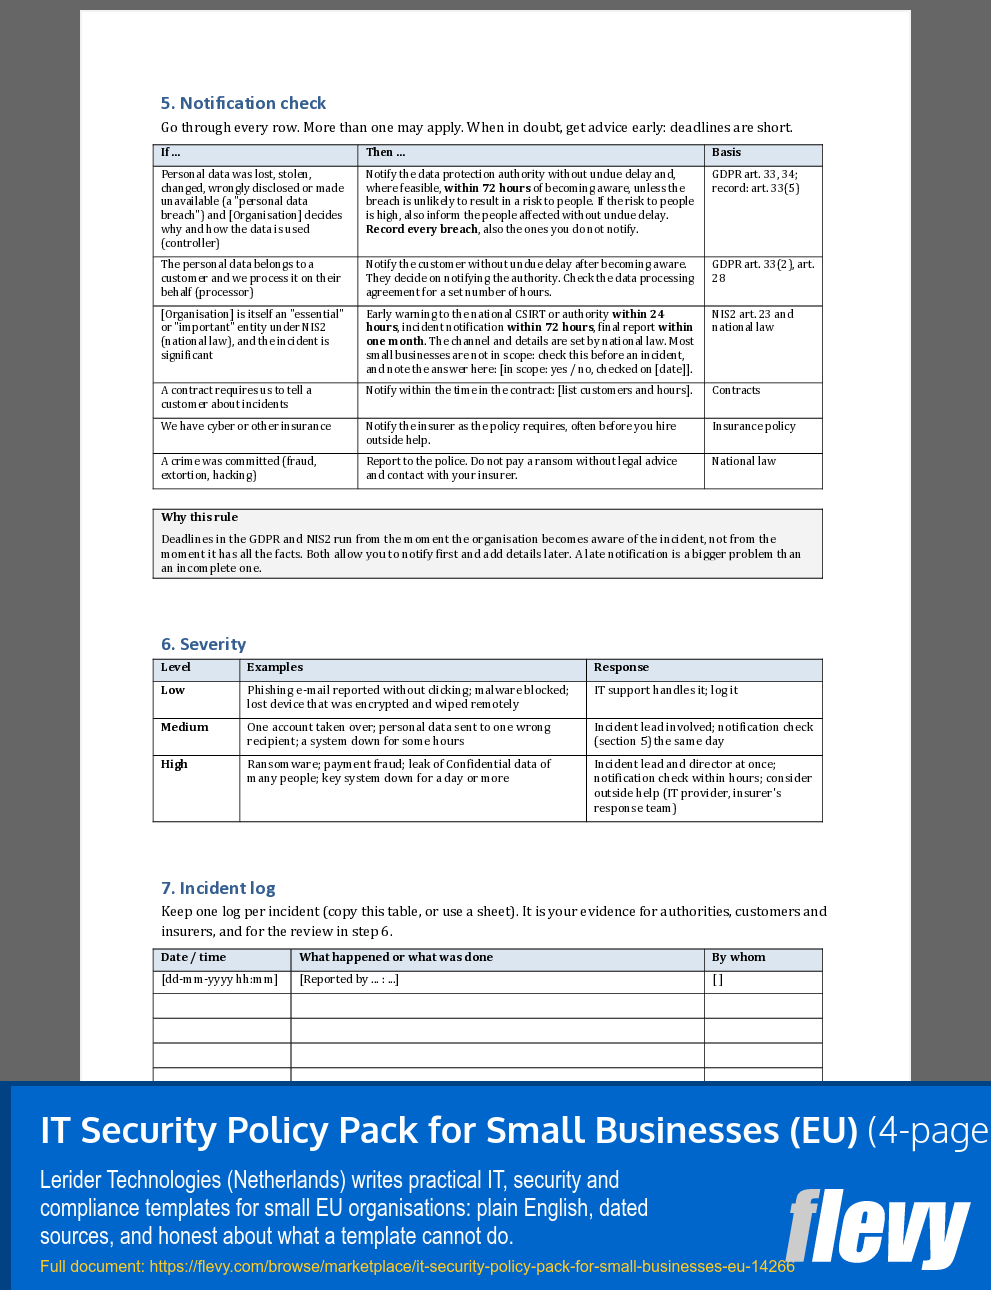
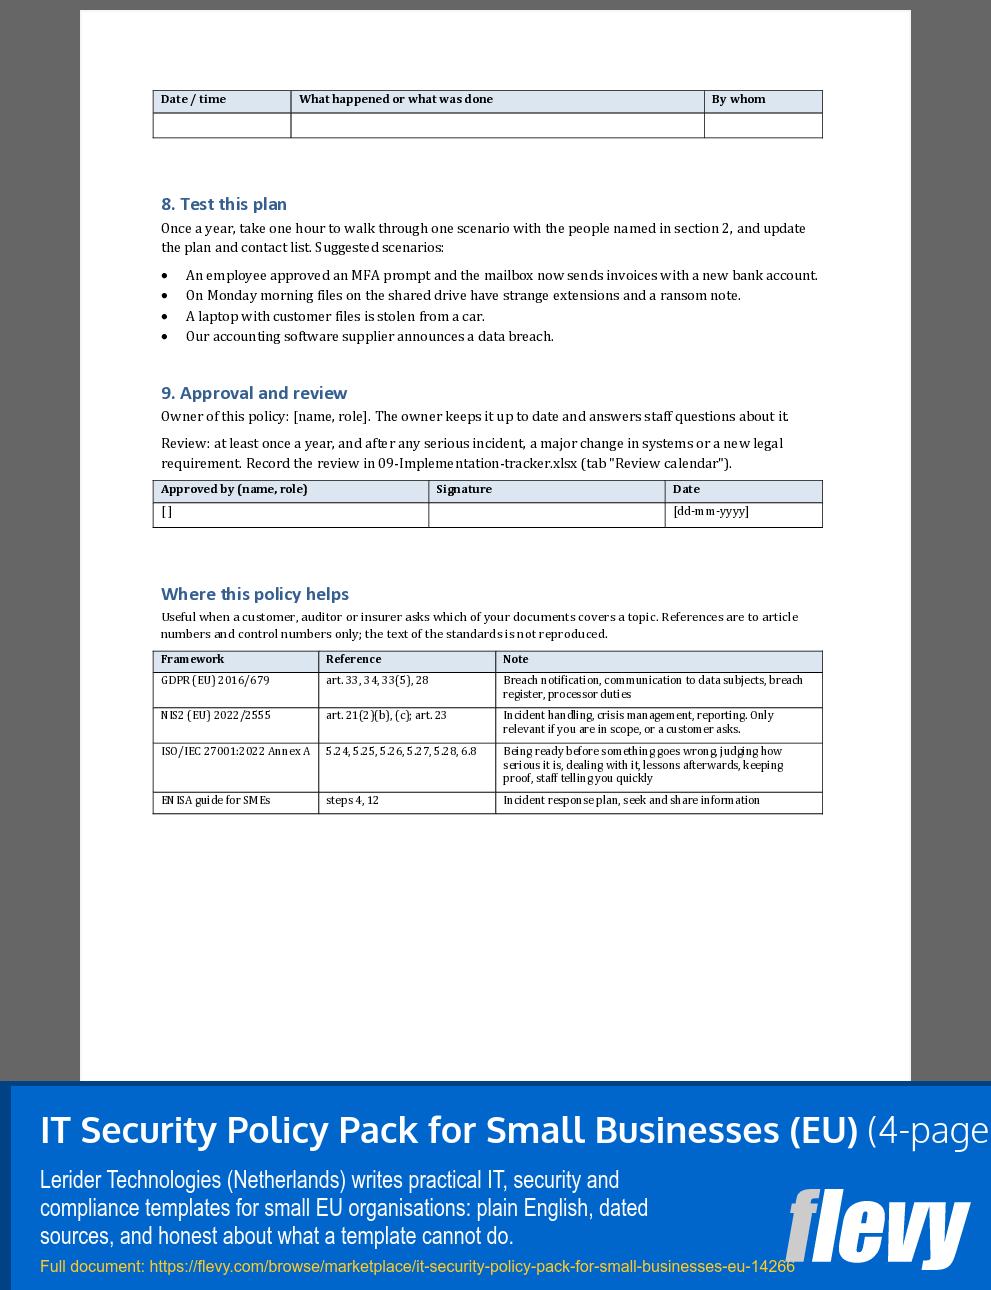
5. Incident response plan (Word): roles, a printable contact list, six steps, and a notification check (GDPR 72 hours, NIS2 24/72 hours if you are in scope, contracts, insurer); severity table, incident log.
6. The 12 rules on one page plus a staff acknowledgement (Word).
7. Joiner / mover / leaver checklist (Excel): 27 IT steps with status and progress, plus a systems list.
8. Supplier risk checklist (Excel): dropdowns, automatic score and priority per supplier.
9. Implementation tracker (Excel): 37 measures with owner, due date, status and evidence, a progress summary, and a review calendar for the recurring tasks (restore tests, access reviews, policy review).
10. One-page action plan (PDF): five steps, about six hours in three sessions.
11. Read me first (Word): how to use the pack, licence, dated source list.
12. Bonus, AI assistant: ready-made prompts to fill in every policy and spreadsheet with Microsoft 365 Copilot, ChatGPT, Le Chat, Claude or Gemini, plus a Claude skill and instructions for your own GPT or Copilot agent. The AI drafts, you check and decide; includes a privacy section (business account, no personal data or system details).
Written for the EU, not adapted from US templates: references to the GDPR and, where relevant, NIS2 art. 21 and 23, plus ENISA and national agency guidance. No US state law, HIPAA or Letter-size pages. Each policy ends with a table that maps it to the GDPR, NIS2 art. 21(2), ISO/IEC 27001:2022 Annex A control numbers and the ENISA SME guide, which helps when a customer sends you a security questionnaire.
This is a template, not legal advice. It does not guarantee compliance with any law or standard, and it is not an ISO 27001 certification kit. Check the sections on monitoring and personal devices against employment rules in your country. Licence: one organisation (including its group companies).
Prepared with AI assistance under Lerider Technologies' direction, and checked against its cited sources before publication. A template, not legal advice.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Cyber Security, Small Business Word: IT Security Policy Pack for Small Businesses (EU) Word (DOCX) Document, Lerider Technologies




























