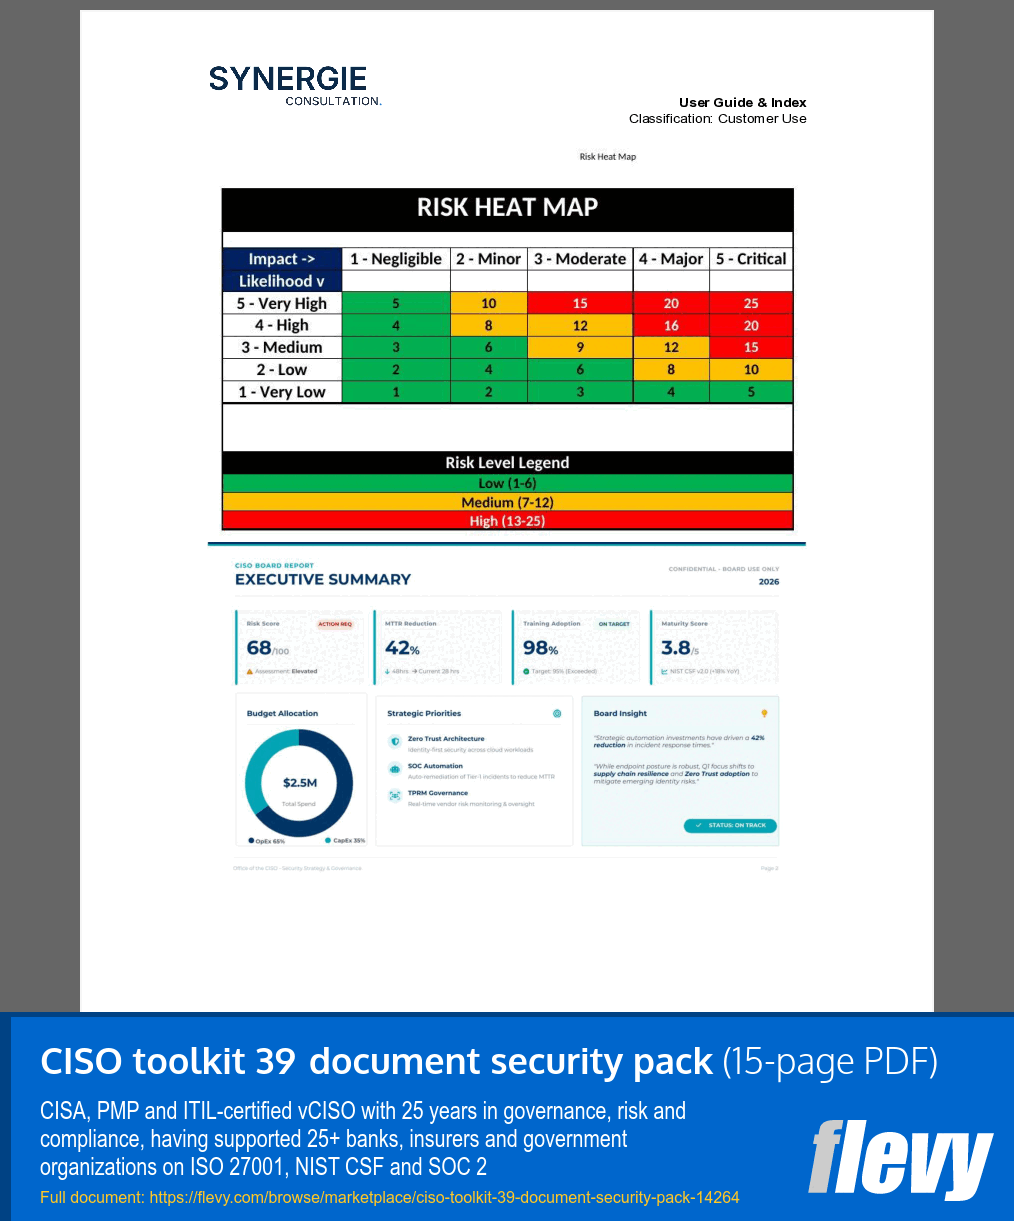
 Click main image to view in full screen. Unlock all 16 preview images:
CISO Toolkit: 39-Document Security Pack – PDF
PDF document + Zip archive file (ZIP) 15 Pages


BENEFITS OF THIS DOWNLOADABLE PDF DOCUMENT
- Gives a new or virtual CISO a complete, consistent documentation baseline in days instead of months
- Helps answer vendor security questionnaires, cyber insurance renewals and ISO 27001 or SOC 2 audit requests with ready-to-adapt evidence
- Equips security leaders to brief the board on risk, strategy and budget with editable, executive-level decks and dashboards
CYBER SECURITY PDF DESCRIPTION
Most organizations do not lack security intentions. They lack documentation. When a client sends a vendor security questionnaire, when the cyber insurer asks for policies at renewal, when an ISO 27001 or SOC 2 auditor requests evidence, or when the board wants a clear view of cyber risk, the same gap appears: the documents either do not exist or are outdated, inconsistent and written by different people over different years.
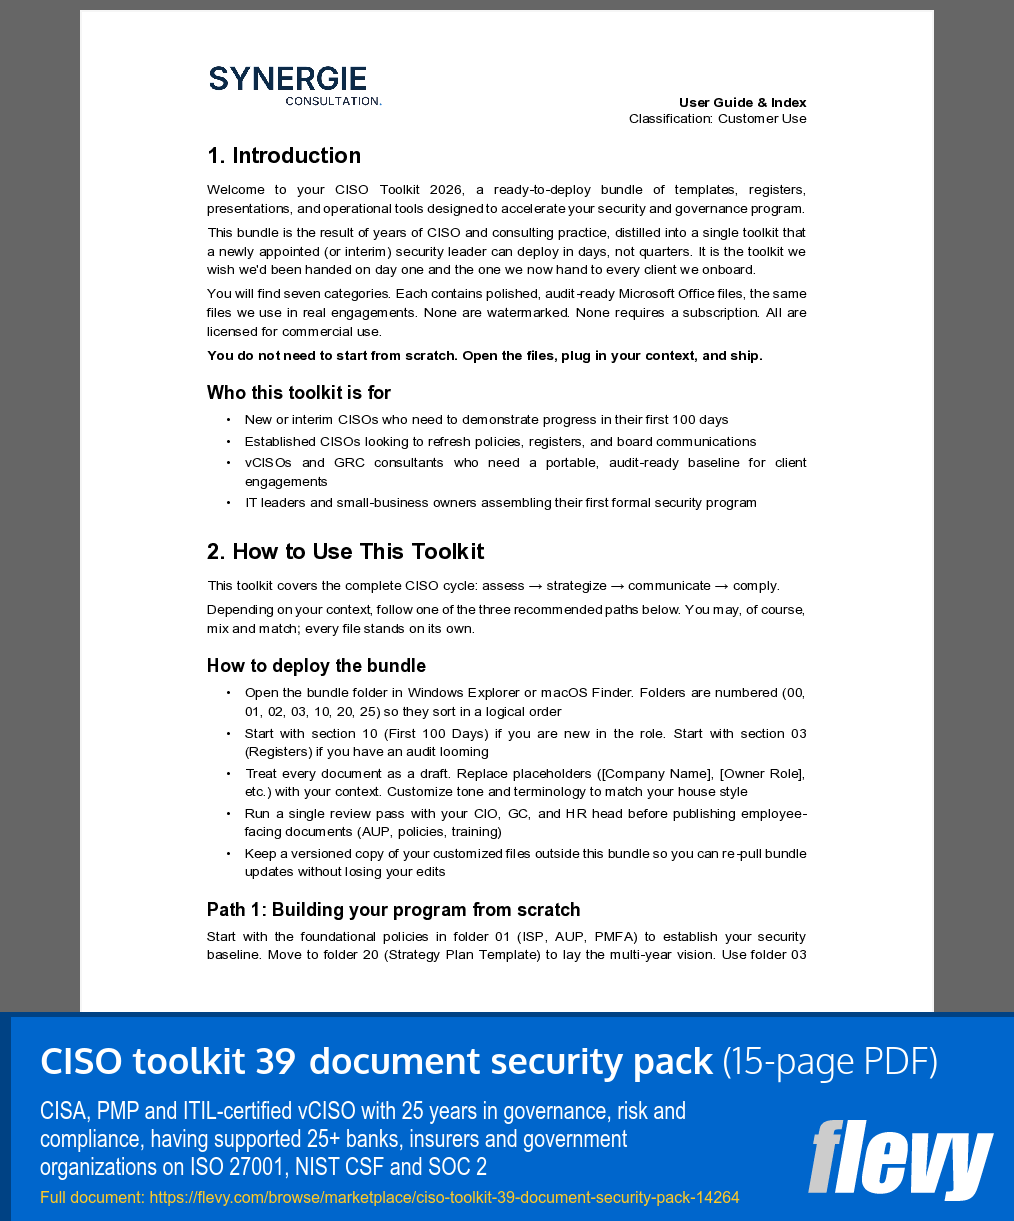
The CISO Toolkit is a set of 39 editable deliverables built by a practicing vCISO with 25 years of experience in governance, risk and compliance. Every document follows the same structure, version control block and classification scheme, so the set reads as one coherent program rather than a collection of unrelated templates.
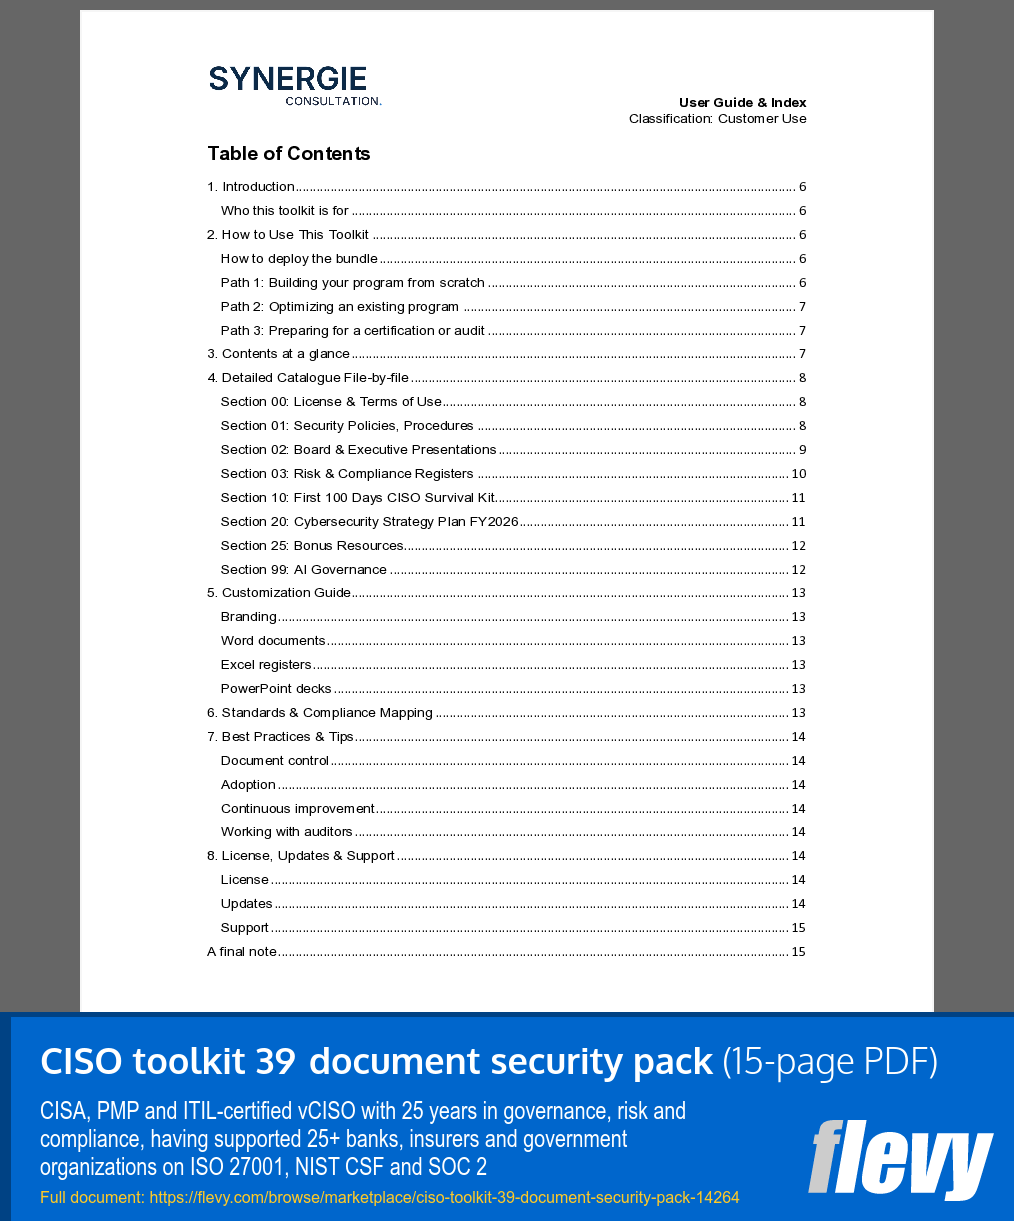
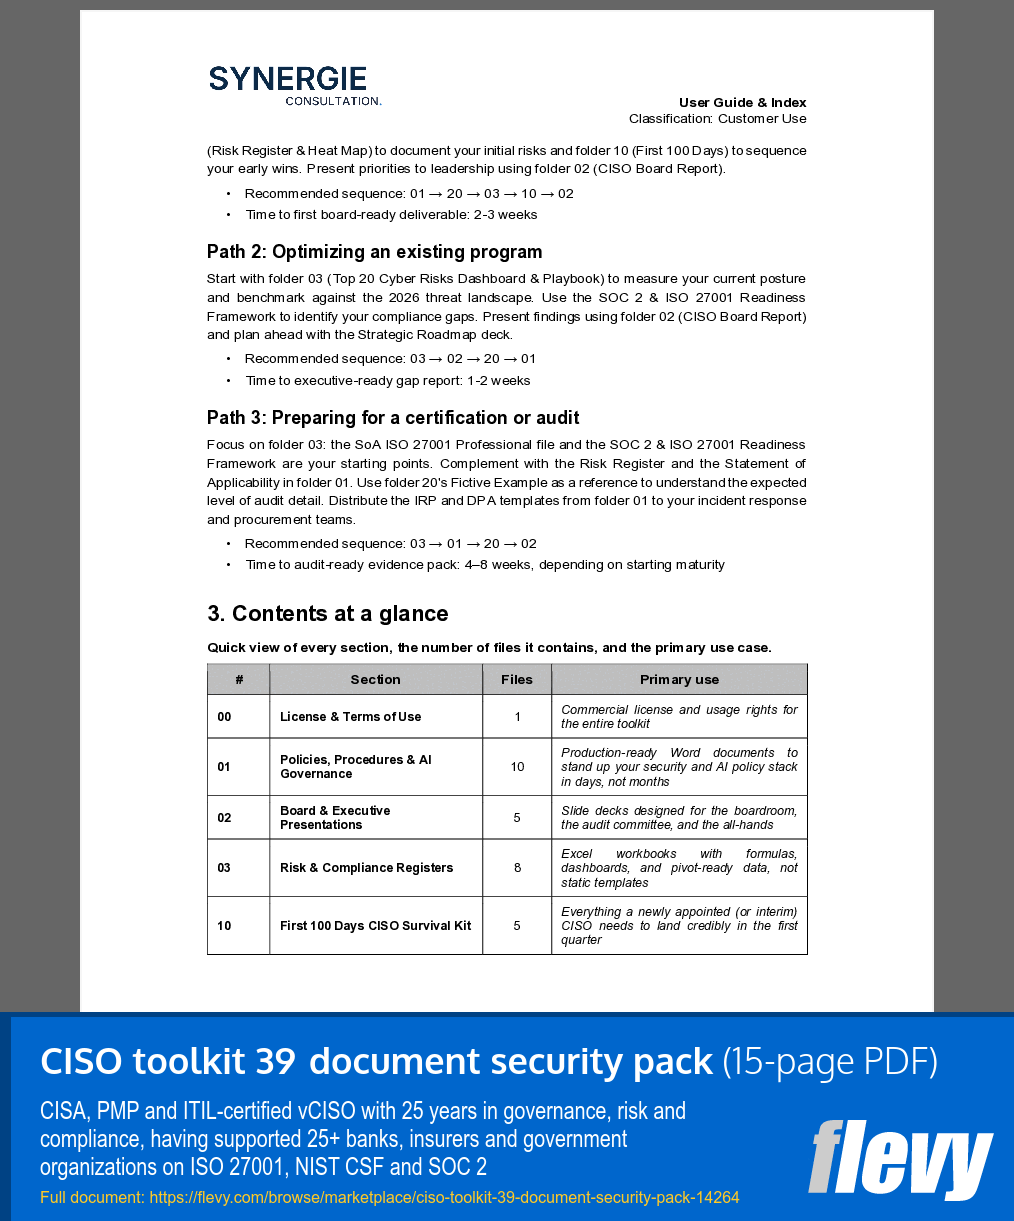
The toolkit is organized into the following folders:
Policies and Procedures (6 documents): Information Security Policy, Acceptable Use Policy, Password and MFA Policy, Incident Response Plan with Crisis Communication, DPA Security Schedule and an ISO 27001:2022 Statement of Applicability.
Board Decks (6 files): CISO Board Report and Strategy 2026 in two visual themes, Tabletop Exercise Kit, Security Awareness Training, Policy Approval Process and a Strategic Roadmap for 2026 to 2027.
Risk and Compliance (8 workbooks): Risk Register and Heat Map in large and small versions, Top 20 Cyber Risks Dashboard and Playbook, ERM Implementation Project Plan, ISO 27001 SoA workbook, SOC 2 and ISO 27001 Readiness Framework, Third-Party Risk Vendor Assessment Questionnaire and a Cybersecurity Business Case ROI and TCO tool.
First 100 Days (5 files): Survival Guide, Board Communication, KPI Dashboard aligned with NIST CSF, Quick Wins Tracker and Stakeholder Engagement Tracker.
Strategy Plan (2 files): a blank template and a fully worked example.
AI Governance (4 documents): AI Policy, AI Acceptable Use Policy, AI Data Handling SOP and AI Tool Request Form, aligned with ISO/IEC 42001.
Bonus Resources (7 files): reference visuals for CIS Controls, AICM and social engineering, a library of 15 security workflows with an editable diagram source, and curated lists of CISO communities and podcasts.
The content is aligned with ISO 27001:2022, SOC 2, NIST CSF 2.0, NIST SP 800-63B and ISO/IEC 42001. All files are in English and fully editable in Word, PowerPoint and Excel.
This toolkit is intended for new or virtual CISOs, IT and security managers in small and mid-sized organizations, GRC consultants and compliance leads preparing for an audit. It provides a professional starting point to adapt to your context; it does not replace a risk assessment specific to your organization and does not by itself confer certification.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Cyber Security, Corporate Policies PDF: CISO Toolkit: 39-Document Security Pack PDF (PDF) Document, Synergie Consultation | Cyber & GRC
ABOUT THE AUTHOR
Security architect and virtual CISO, CISA certified, with 20+ years of experience designing, implementing and auditing cybersecurity, IT governance and risk management programs in highly regulated environments.
I have worked on security and compliance initiatives for major Canadian organizations, including National Bank, Beneva, TELUS, DMR and CAA Québec. This background helps executives turn
... [read more]
Ask the Author a Question
You must be logged in to contact the author.




























