 Click main image to view in full screen.
Cyber Risk Register and Board Reporting Kit – Word DOCX
Word (DOCX) + Zip archive file (ZIP) 3 Pages


BENEFITS OF THIS DOWNLOADABLE WORD DOCUMENT
- Brings business scenarios, owners, evidence and decision requests together in one register.
- Summarises active risks and distinguishes overdue actions from overdue reviews.
- Provides a blank workbook, fictional worked example and practical Word guidance.
RISK MANAGEMENT WORD DESCRIPTION
An editable Excel and Word toolkit for security leads, fractional CISOs and MSP practitioners preparing cyber risk information for one organisation. It provides a structured register, a calculated board summary, a fictional worked example and a manually maintained board report. Buyers can start with the example to understand the workflow, then adapt the blank workbook for their own internal use.
The blank workbook contains 100 risk-record slots. Records capture business scenarios, owners, existing controls, evidence references, initial and current assessments, response actions, due dates, review dates and decision requests. Current likelihood and impact use a five-by-five scoring approach. The bands are prioritisation defaults, not financial-loss estimates or measured probabilities.
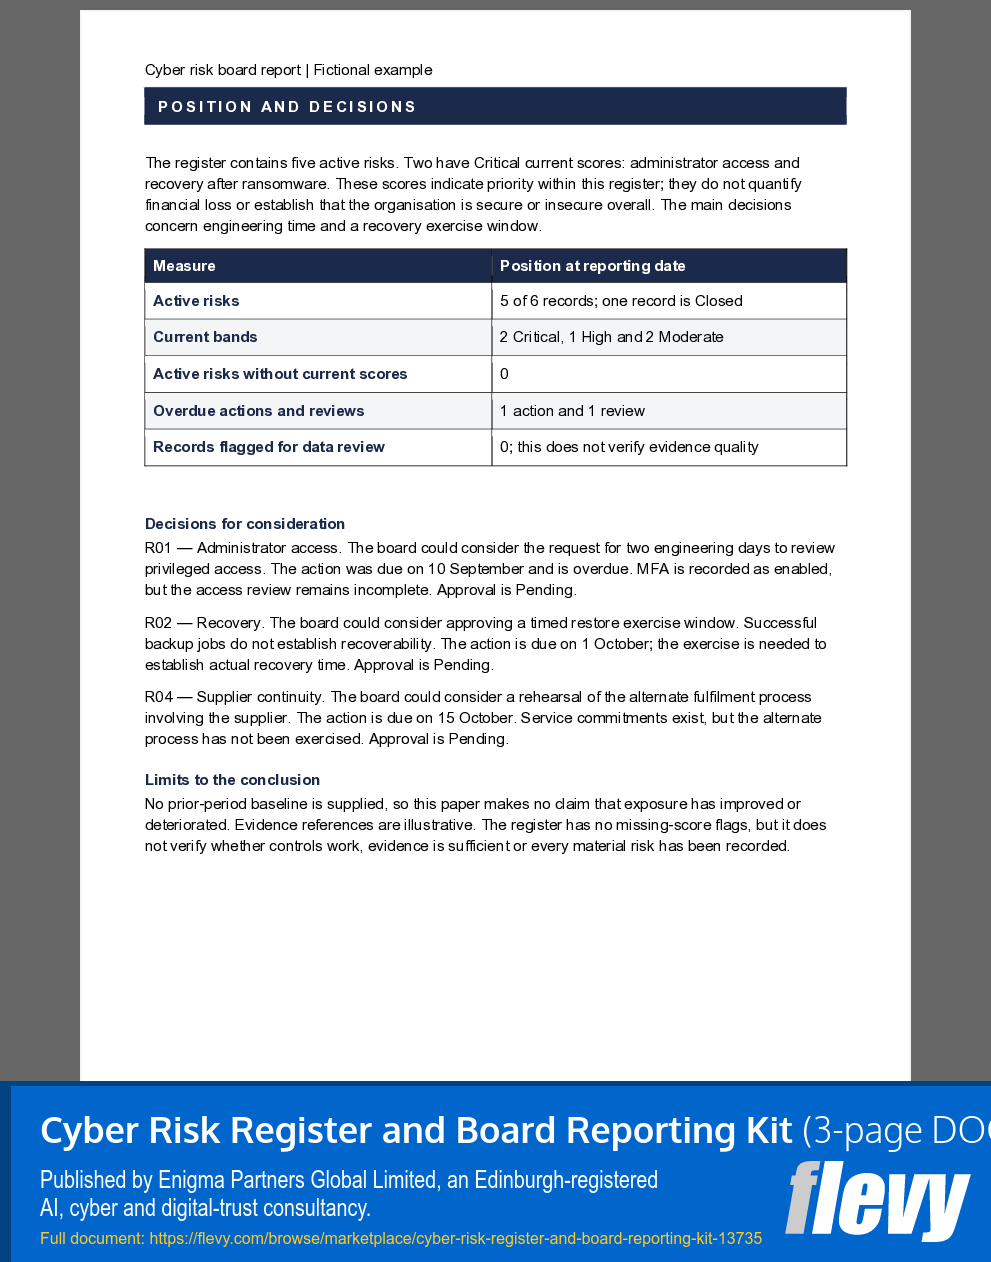
The board summary calculates active-risk counts, current risk bands, overdue actions and reviews, and the five highest-scored active records. Closed risks are excluded from active counts; Accepted risks remain active. Missing or invalid current scores remain unscored rather than becoming zero. A data-review field flags detected input issues, but cannot establish whether supporting evidence is accurate or sufficient.
The worked workbook contains six fictional risks. It demonstrates how a risk score can sit alongside a business consequence, a decision request and remaining uncertainty. The primary document is the worked Word board report. The secondary ZIP contains the complete kit: two XLSX workbooks, Start_Here.docx, Board_Report_Worked_Example.docx and a release manifest. The report is included in both locations for convenience. The guide explains the workflow, common questions and single-organisation licence.
There are no macros or required add-ins. Word report figures and narrative are updated manually; no live Excel-to-Word connection or automatic historical trends are included. Formula behaviour has been checked in Windows Excel and LibreOffice. Excel for Mac and Google Sheets have not been independently verified.
The licence permits internal use, adaptation and rebranding for one named organisation, including work by its employees and contractors. A consultant may use the kit for that licensed client. Additional organisations require additional licences. The source templates may not be resold, sublicensed or publicly redistributed. Consultancy, custom configuration, audit certification and lifetime updates are not included. All demonstration scenarios and evidence references are fictional.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Risk Management, Cyber Security Word: Cyber Risk Register and Board Reporting Kit Word (DOCX) Document, Enigma CISO Tools