 Click main image to view in full screen.
Post-Quantum Cryptography Readiness Assessment Tool – Excel XLSX
Excel (XLSX) + Excel (XLSX)


BENEFITS OF THIS DOWNLOADABLE EXCEL DOCUMENT
- Assess PQC readiness across 46 weighted questions in 6 domains, aligned with the G7/ANSSI Sept. 2026 Call to Action -- get an auto-scored dashboard, radar/gauge charts, and automatically flagged weak areas instead of a static, one-size-fits-all checklist.
- Reuse this assessment as compliance evidence: all 46 questions are cross-mapped to ISO/IEC 27001, DORA, NIS2, SOC 2, and HIPAA -- turning one PQC self-assessment into supporting documentation for five other frameworks you may already be tracking.
- Go from score to action: an auto-generated Executive Summary for the board, a tracked Action Plan with owners and due dates, and Trend Tracking to log progress every cycle -- so results turn into a documented program, not just a one-time number.
MATURITY MODEL EXCEL DESCRIPTION
WHAT IS THIS POST-QUANTUM CRYPTOGRAPHY (PQC) READINESS ASSESSMENT TOOL FOR?
It is a complete, structured self-assessment that helps any organization evaluate its readiness for the transition to post-quantum cryptography – from cryptographic inventory to board-ready reporting – aligned with the G7/ANSSI "Preparing for the Post-Quantum Era: A Call to Action" (September 2026) and cross-mapped to ISO/IEC 27001:2022, DORA, NIS2, SOC 2, and HIPAA.
Stop building your PQC governance tracker from scratch. This Excel tool gives you a scored, weighted, 46-question assessment across 6 domains, an auto-calculated dashboard with radar and gauge charts, a board-ready executive summary, a tracked action plan, and a crosswalk that lets you reuse the results as evidence in an existing ISMS, SOC 2, or HIPAA compliance file.
Created by a former CISO with 15+ years of experience in critical infrastructure security, this is a single, self-contained Excel workbook – no macros, no subscriptions, ready to use immediately – plus a fully completed sample workbook so you can see exactly what a finished assessment looks like before you fill in your own.
________________________________________
AT A GLANCE (KEY SPECIFICATIONS)
• Framework Alignment: G7/ANSSI "Preparing for the Post-Quantum Era: A Call to Action" (Sept. 2026); cross-mapped to ISO/IEC 27001:2022 Annex A, DORA (EU 2022/2554), NIS2 Directive Article 21(2), SOC 2 (AICPA Trust Services Criteria), and the HIPAA Security Rule (45 CFR 164.308/310/312)
• Target Audience: CISOs, Compliance Officers, Information Security Managers, Internal Auditors, GRC Professionals, Consultants
• File Format: Editable .XLSX (10 sheets, macro-free), tested on Office 2010+
• Key Features: 46-question weighted gap assessment across 6 domains, auto-flagged weak areas, board-ready Executive Summary, radar + gauge dashboard, Action Plan generator with Priority and Status pie charts, Trend Tracking, 5-framework Standards Crosswalk, Sector Weighting Guide
________________________________________
WHY CHOOSE THIS TOOL?
Built Around a Named, Dated, International Call to Action Most PQC content is vague "quantum is coming" messaging. This tool is structured directly around the G7 Cybersecurity Working Group's September 2026 report, co-signed by France (ANSSI), Canada, Germany, Italy, Japan, the UK, and the US – following its recommended progressive approach: inventory, dependency mapping, risk assessment, and transition planning.
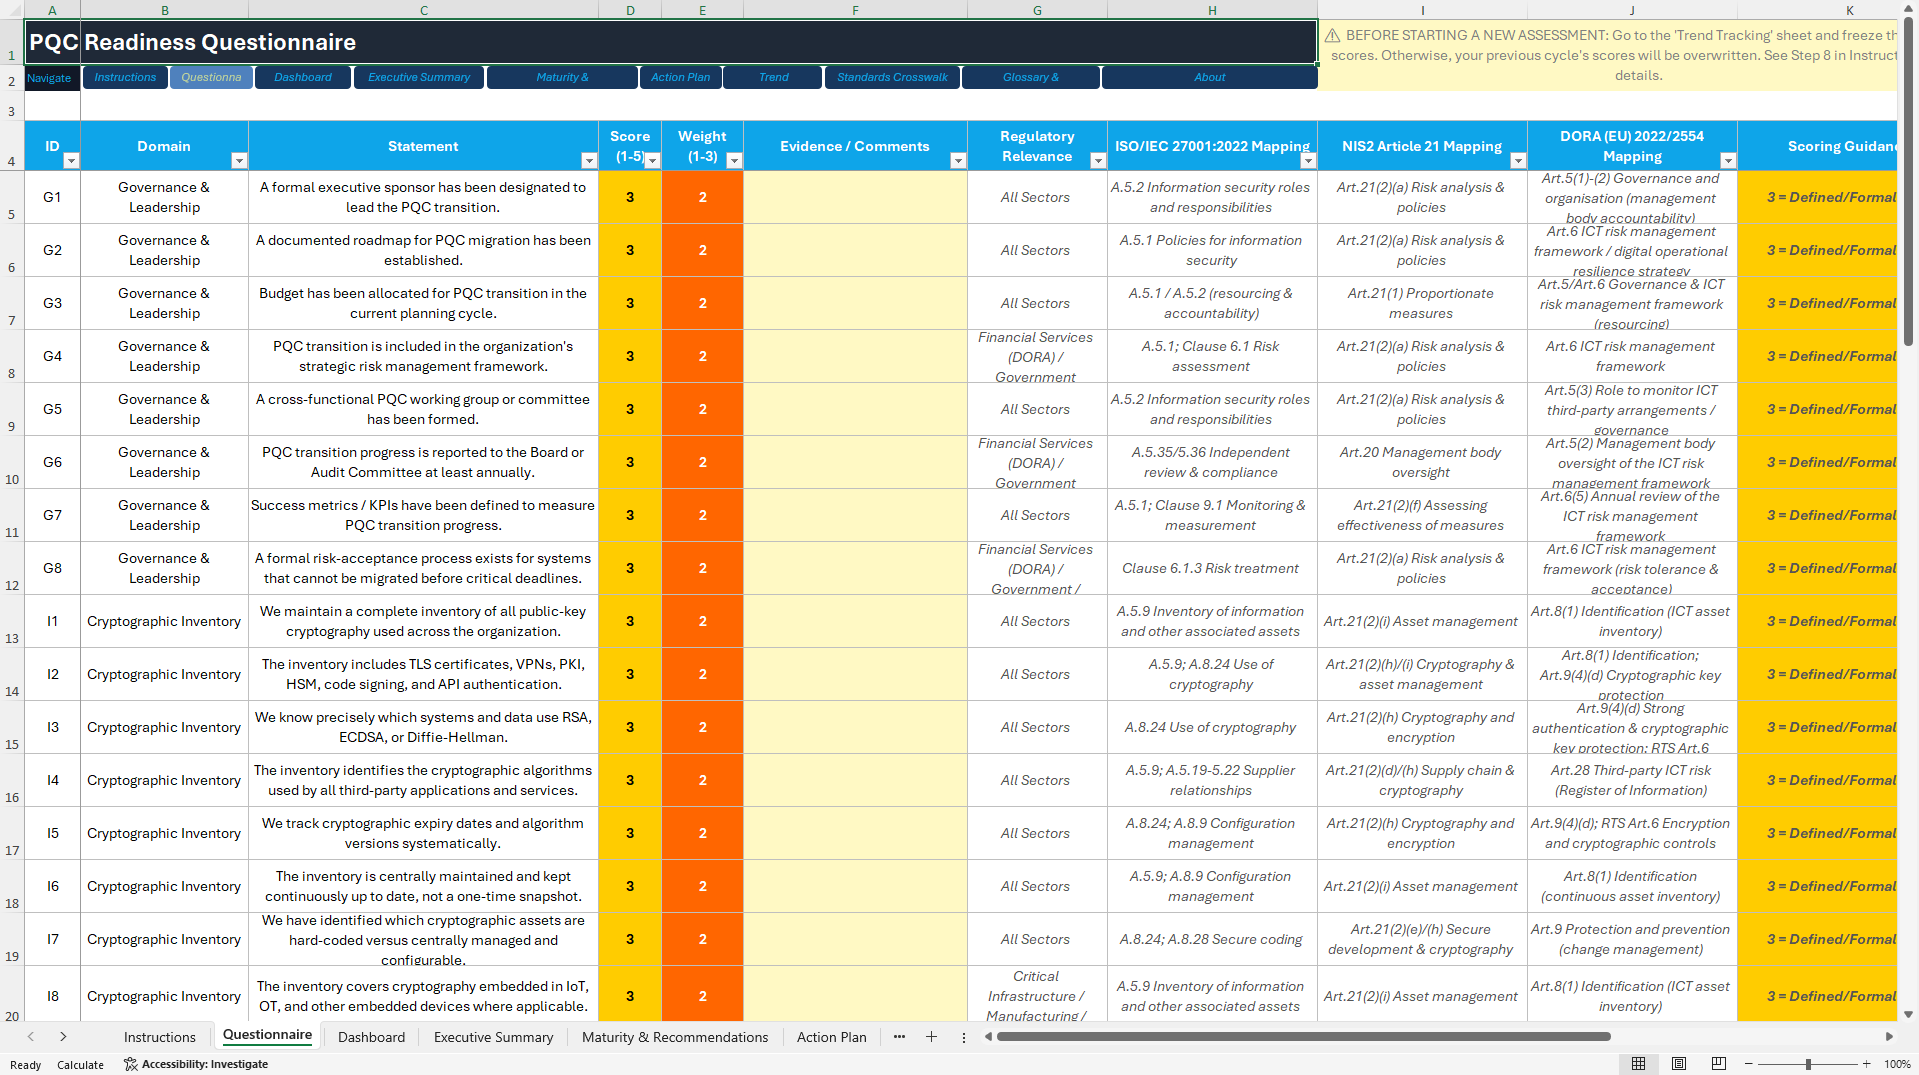
46-Question Weighted Assessment, Not a Flat Checklist Six domains (Governance & Leadership, Cryptographic Inventory, Risk Assessment, Technical Preparedness, Suppliers & Supply Chain, Skills & Awareness), each with a 1-5 maturity scale. Every question carries its own editable Weight (1-3), so domain and overall scores are true weighted averages – not every question forced to count equally regardless of how material it is to your organization.
Evidence-Backed, Not Just Scored Every question has an Evidence/Comments field, so a score of "3" is backed by a policy name, a system reference, or a documented reason – exactly what an internal or external reviewer will ask for later.
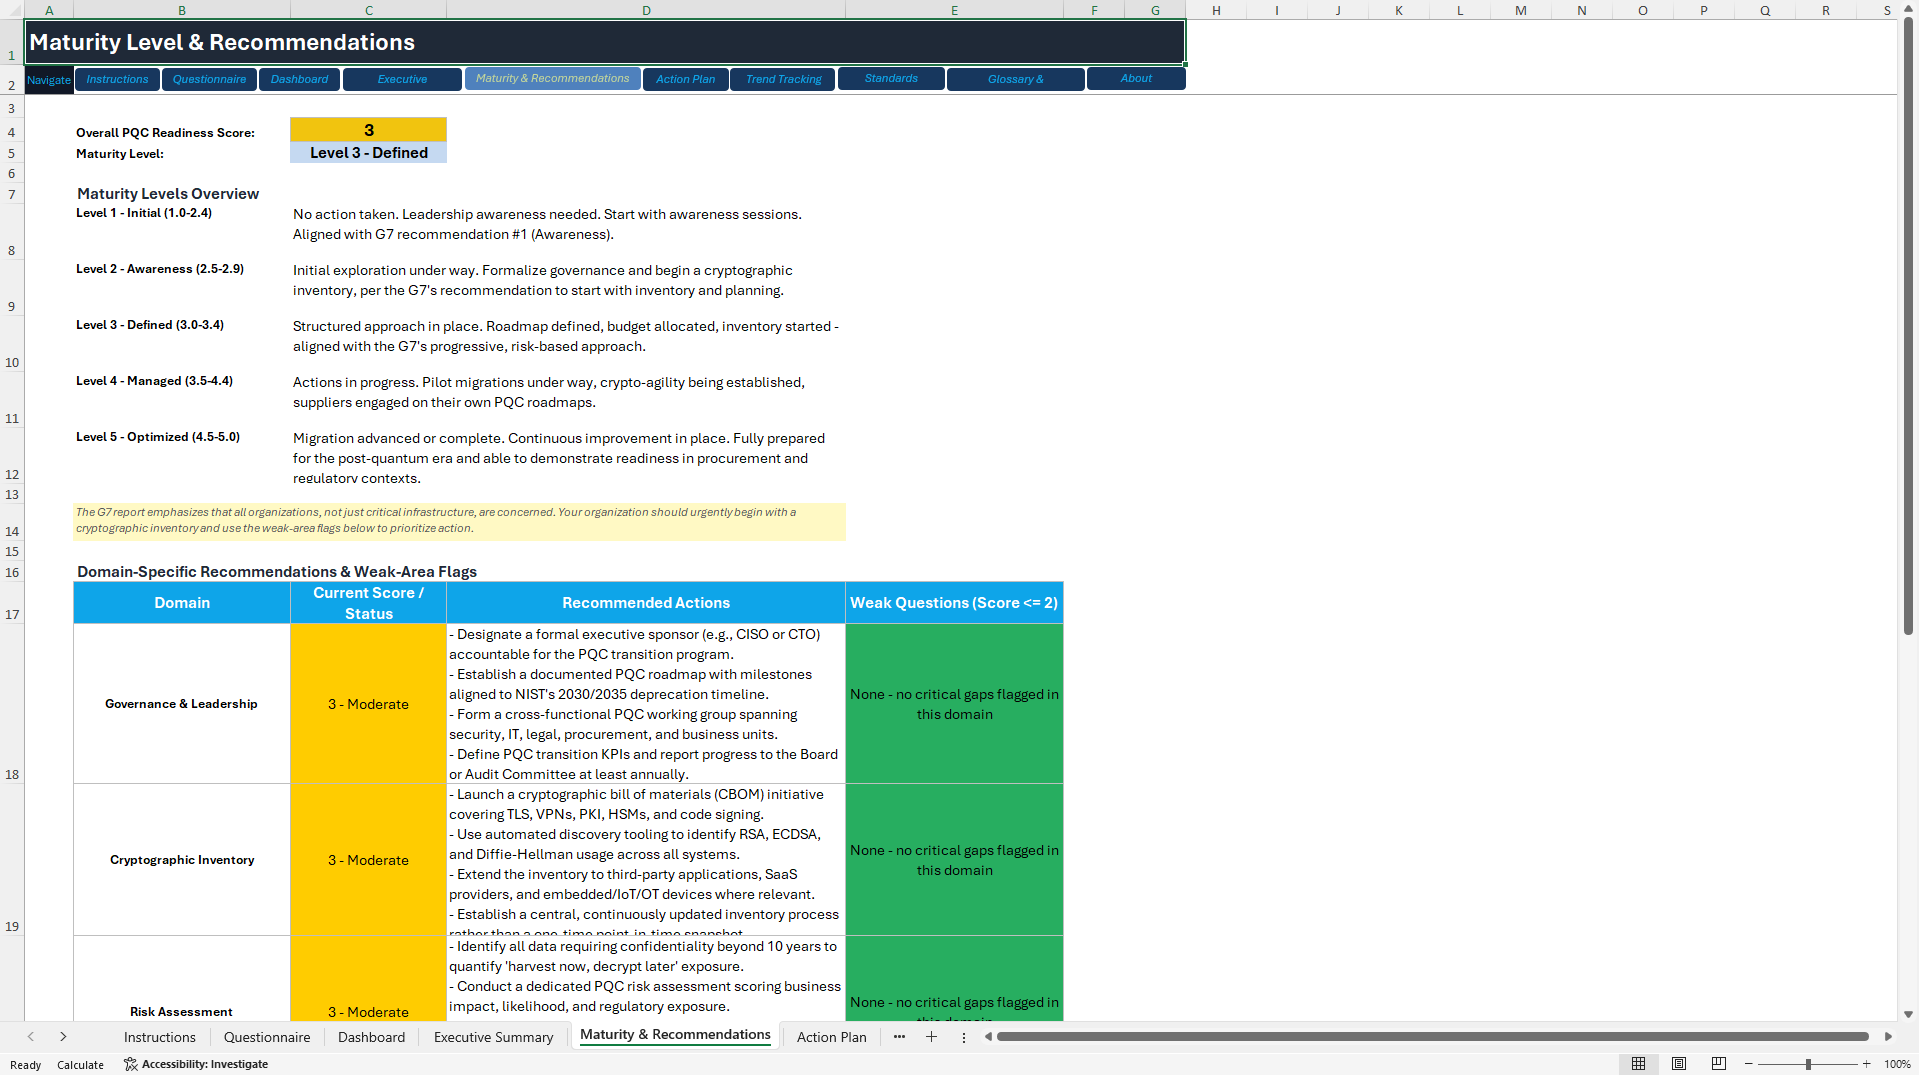
Automatically Flagged Weak Areas Rather than one generic recommendation block per domain, the Maturity sheet formula-detects and lists the exact question IDs scoring 2 or below in each domain – so the output tells you specifically what's missing, not just that a domain is "moderate."
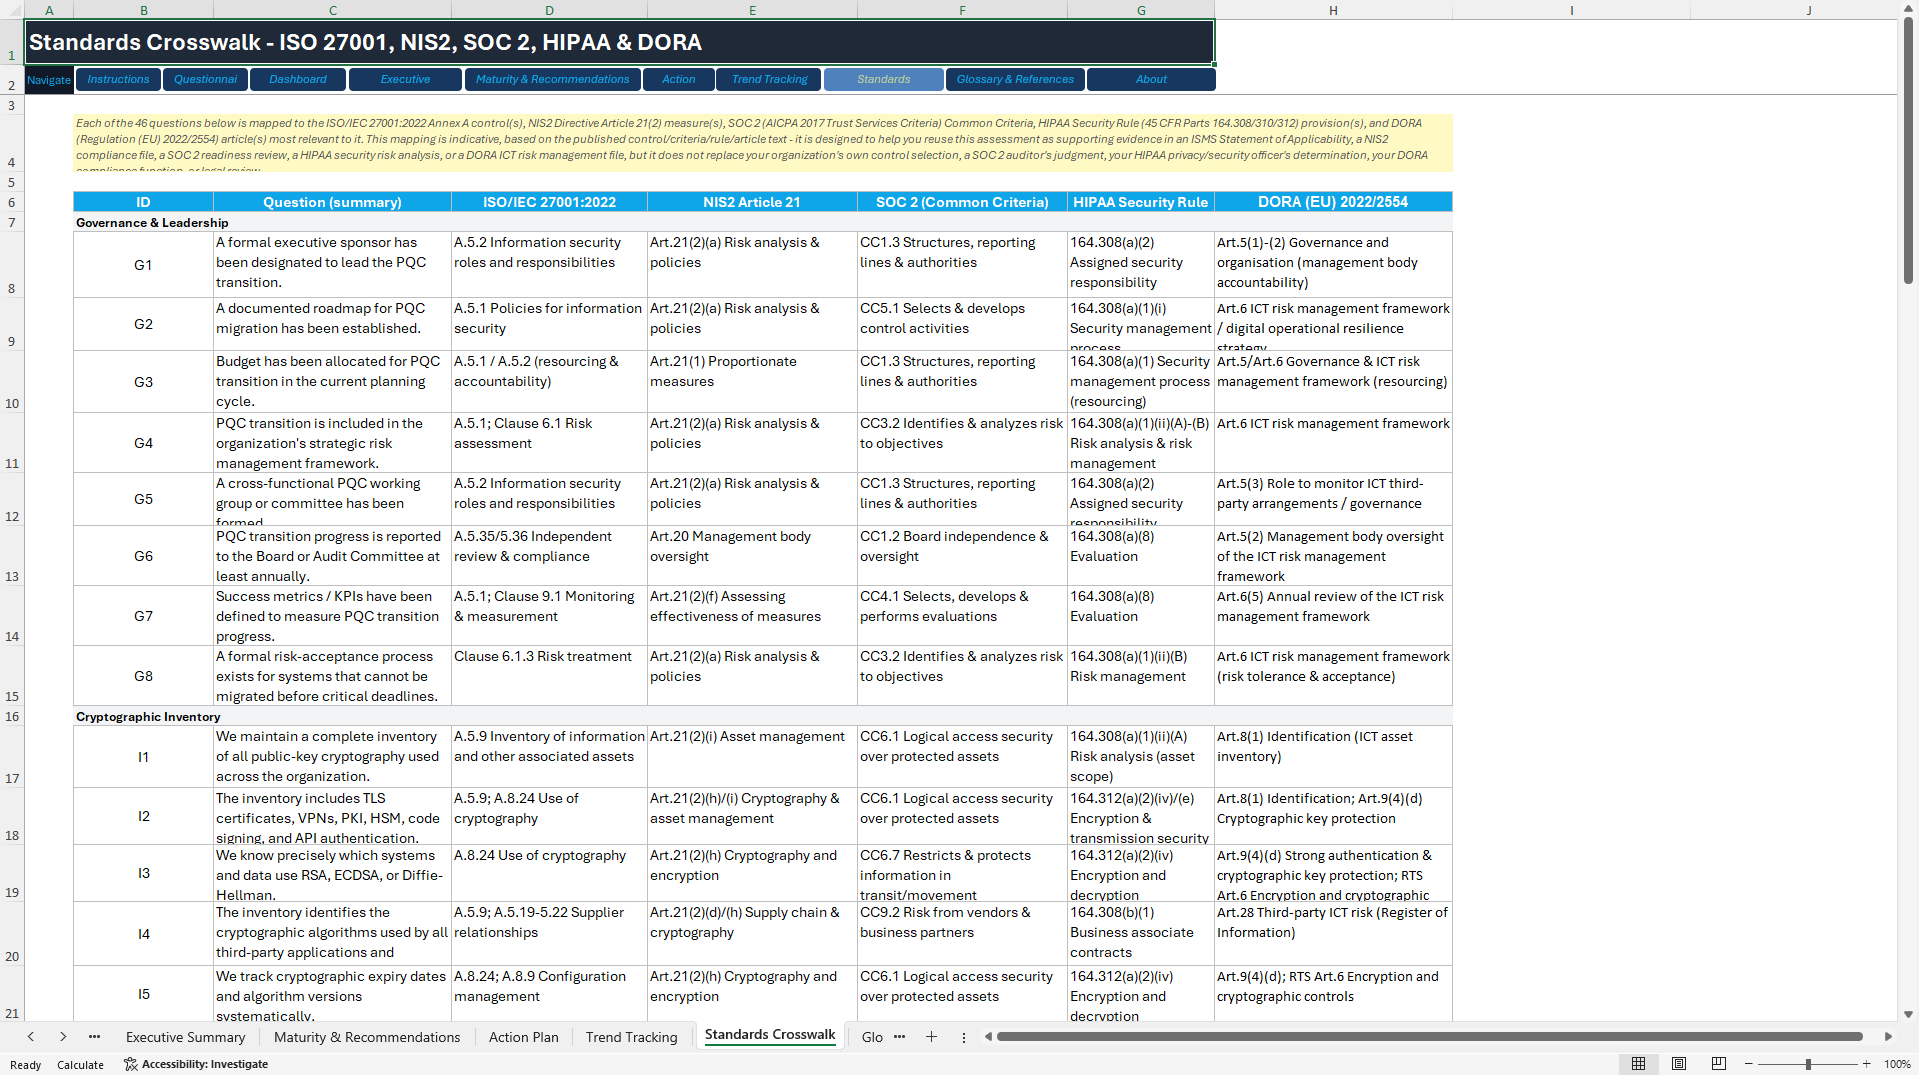
Five-Framework Standards Crosswalk Every one of the 46 questions is mapped to the ISO/IEC 27001:2022 Annex A control(s), DORA (Regulation (EU) 2022/2554) article(s), NIS2 Directive Article 21(2) measure(s), SOC 2 Common Criteria, and HIPAA Security Rule provision(s) most relevant to it – verified against the published control/criteria/rule/article text. Reuse this assessment as supporting evidence in your ISMS Statement of Applicability, DORA ICT risk management file, NIS2 compliance file, SOC 2 readiness review, or HIPAA risk analysis.
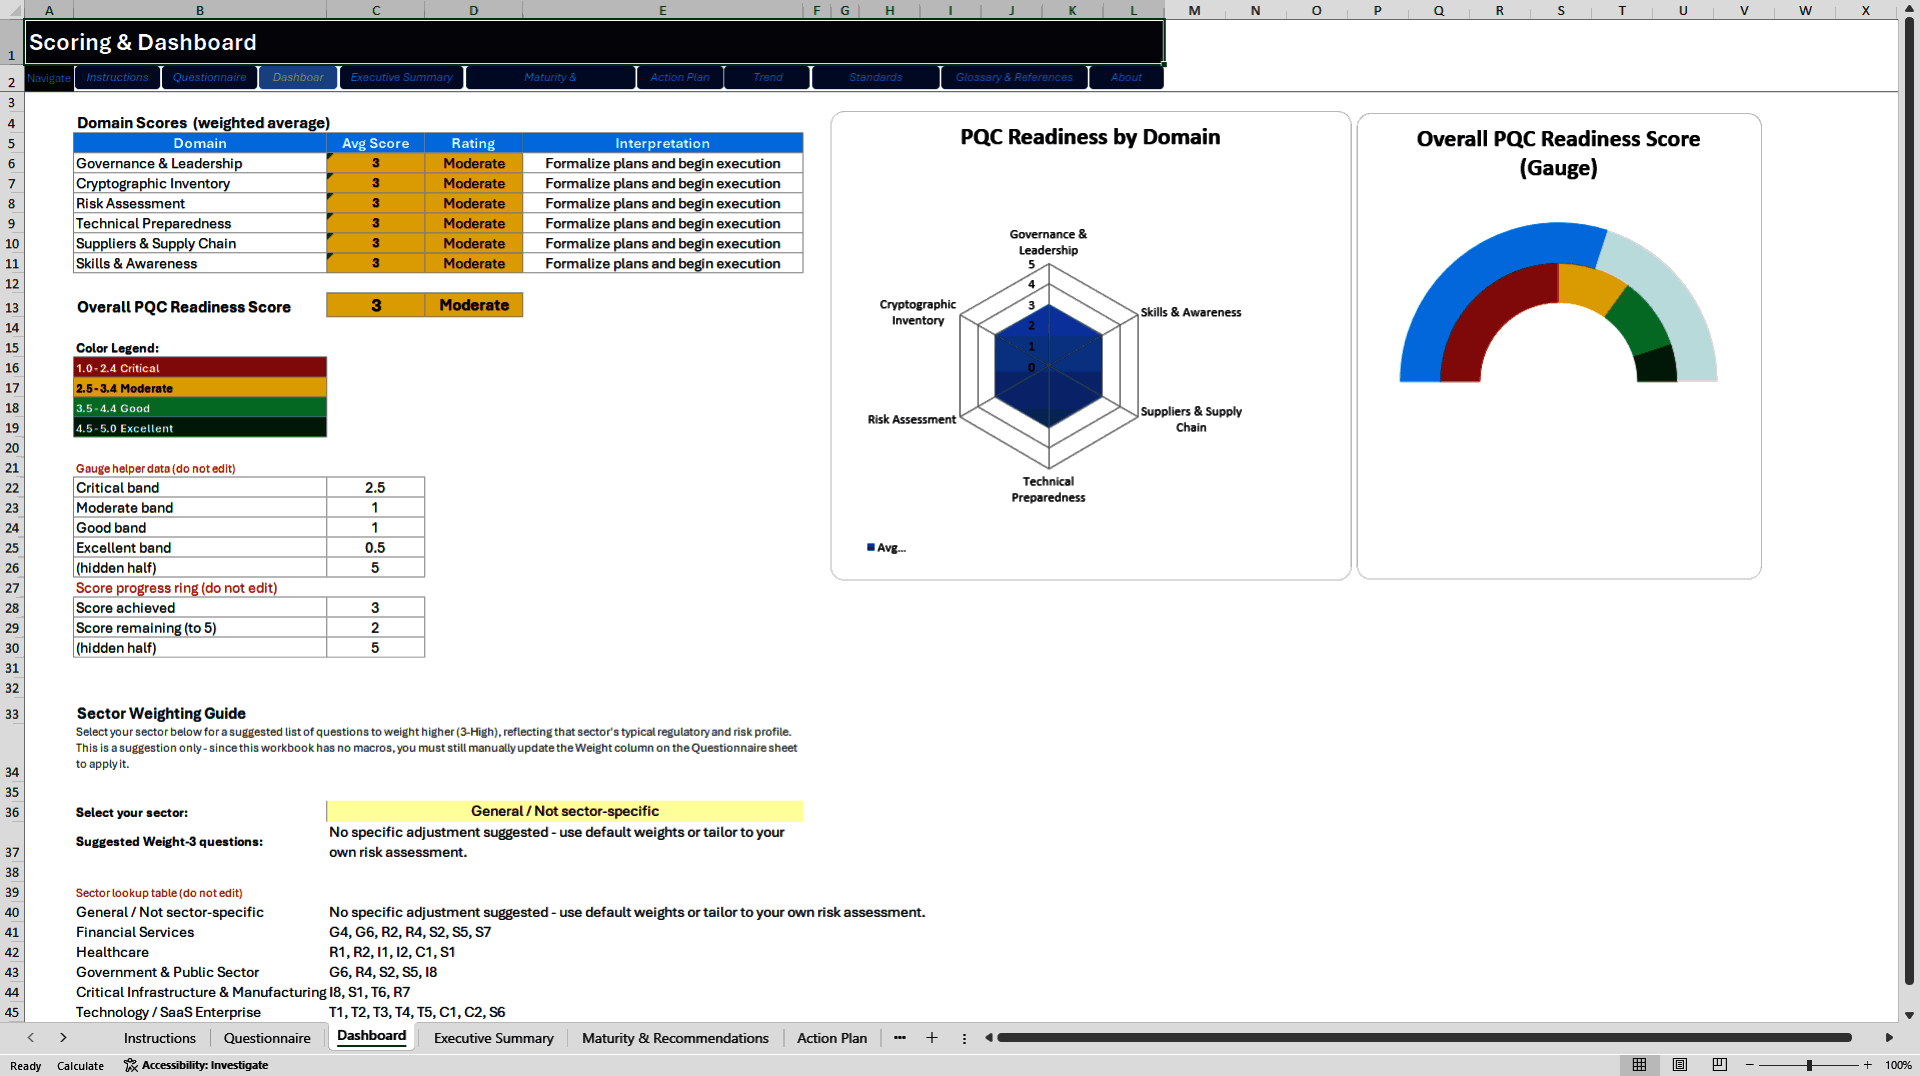
Sector Weighting Guide Select your sector (Financial Services, Healthcare, Government & Public Sector, Critical Infrastructure & Manufacturing, Technology/SaaS Enterprise) from a dropdown on the Dashboard, and get a suggested list of which questions to weight higher, reflecting that sector's typical regulatory and risk profile – and for Financial Services specifically, a set of questions that also carry direct DORA article mappings in the crosswalk.
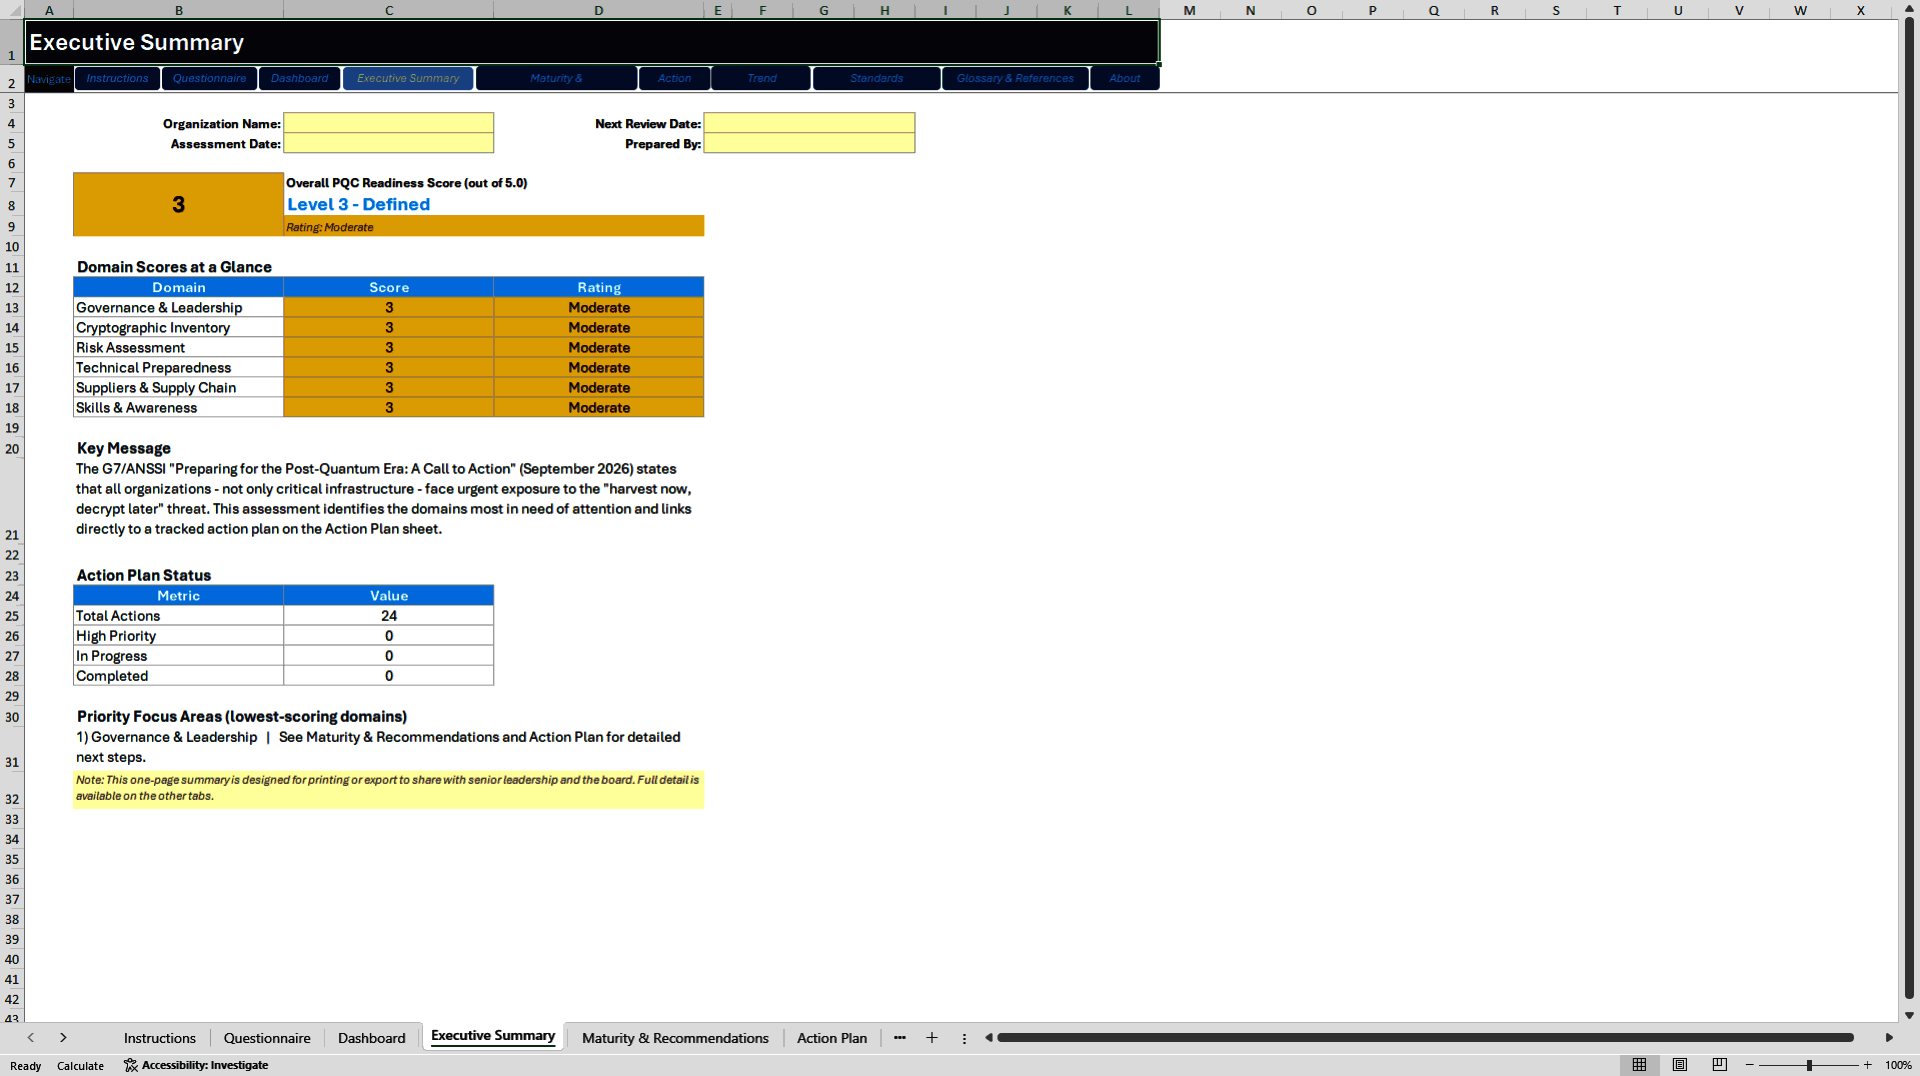
Board-Ready in One Click of a Tab The Executive Summary sheet gives a printable one-pager: overall score, maturity level, domain scorecard, and an auto-identified lowest-scoring priority domain – pulled live via formula, not manually curated.
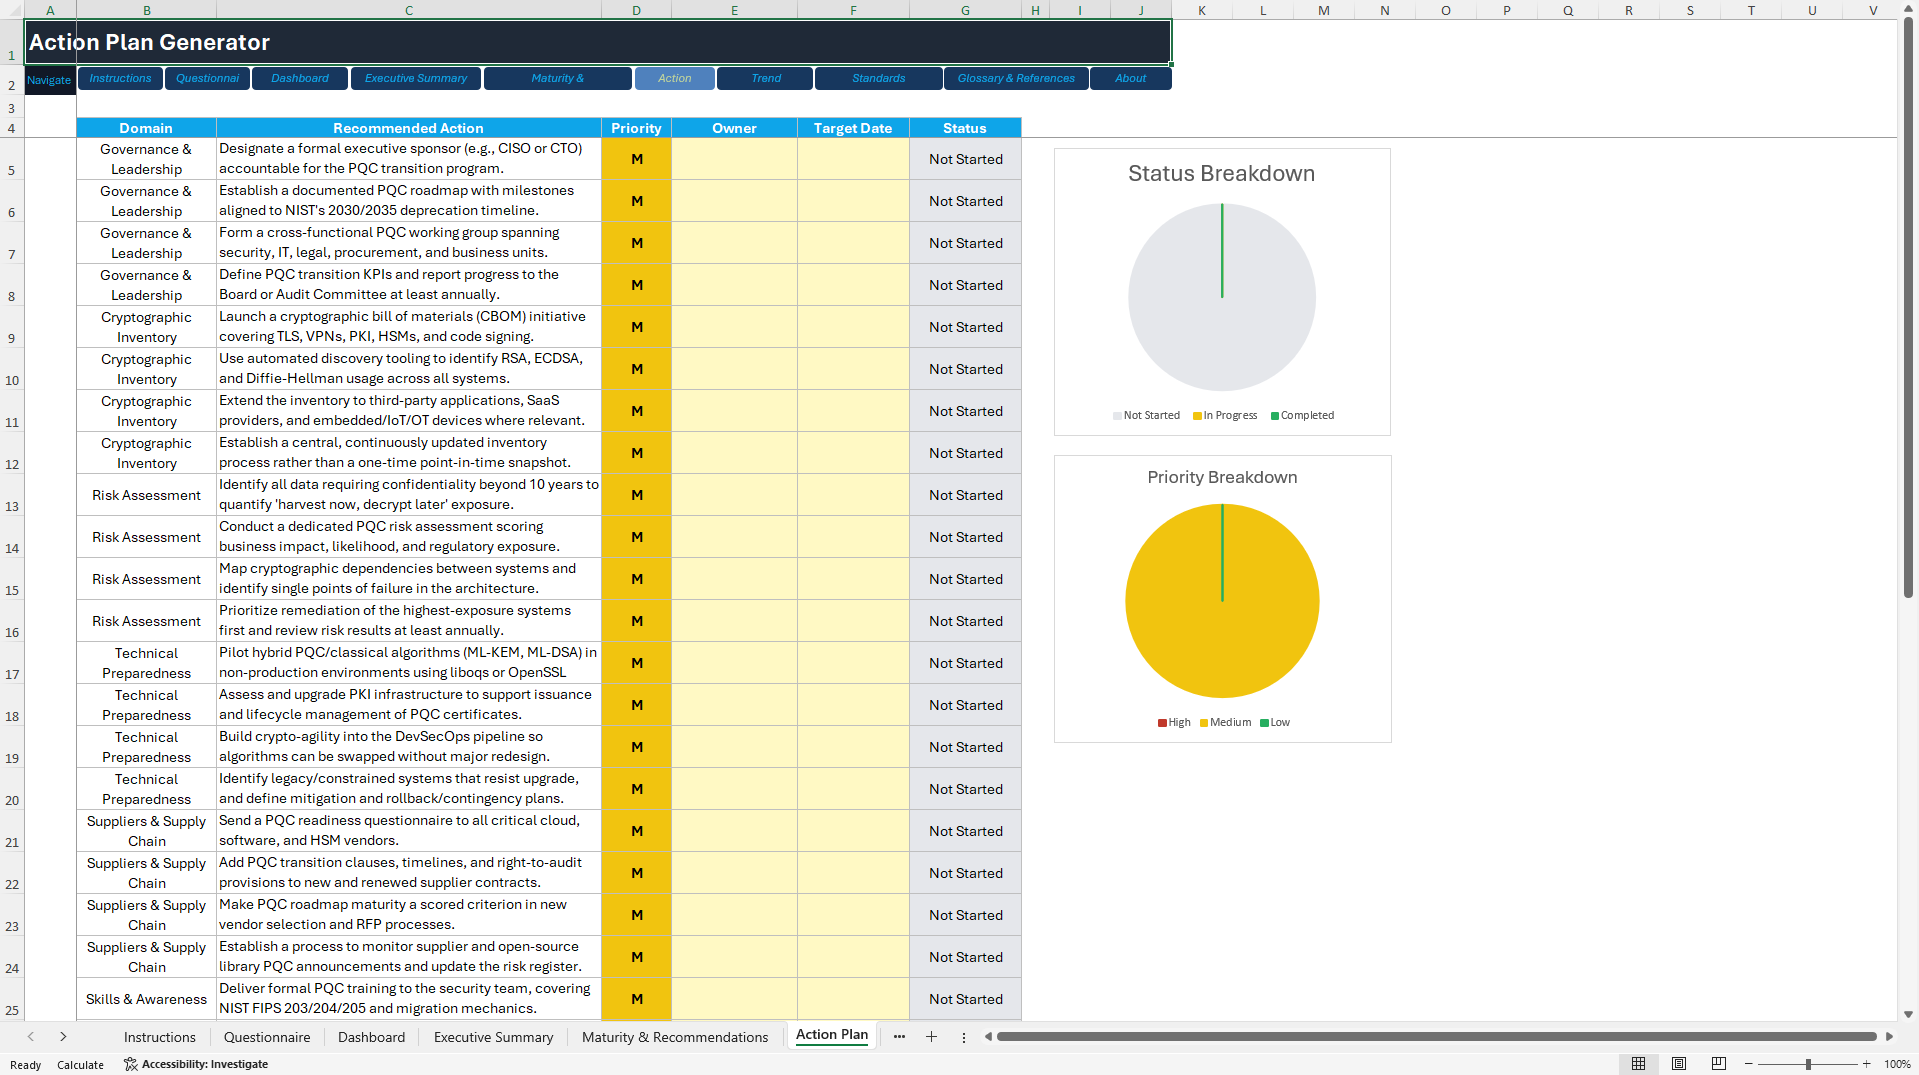
Tracked Action Plan with Executive Dashboard, Not Just Recommendations – Every recommendation is pre-loaded into an Action Plan sheet with auto-calculated Priority (High/Medium/Low, based on the related domain's score) plus editable Owner, Target Date, and Status (dropdown) columns. Two live pie charts – a Priority Breakdown showing the distribution of High/Medium/Low actions, and a Status Breakdown showing how many actions are Not Started, In Progress, or Completed – update automatically as you edit the plan, giving leadership a board-ready view of workload and execution progress without any manual chart work.
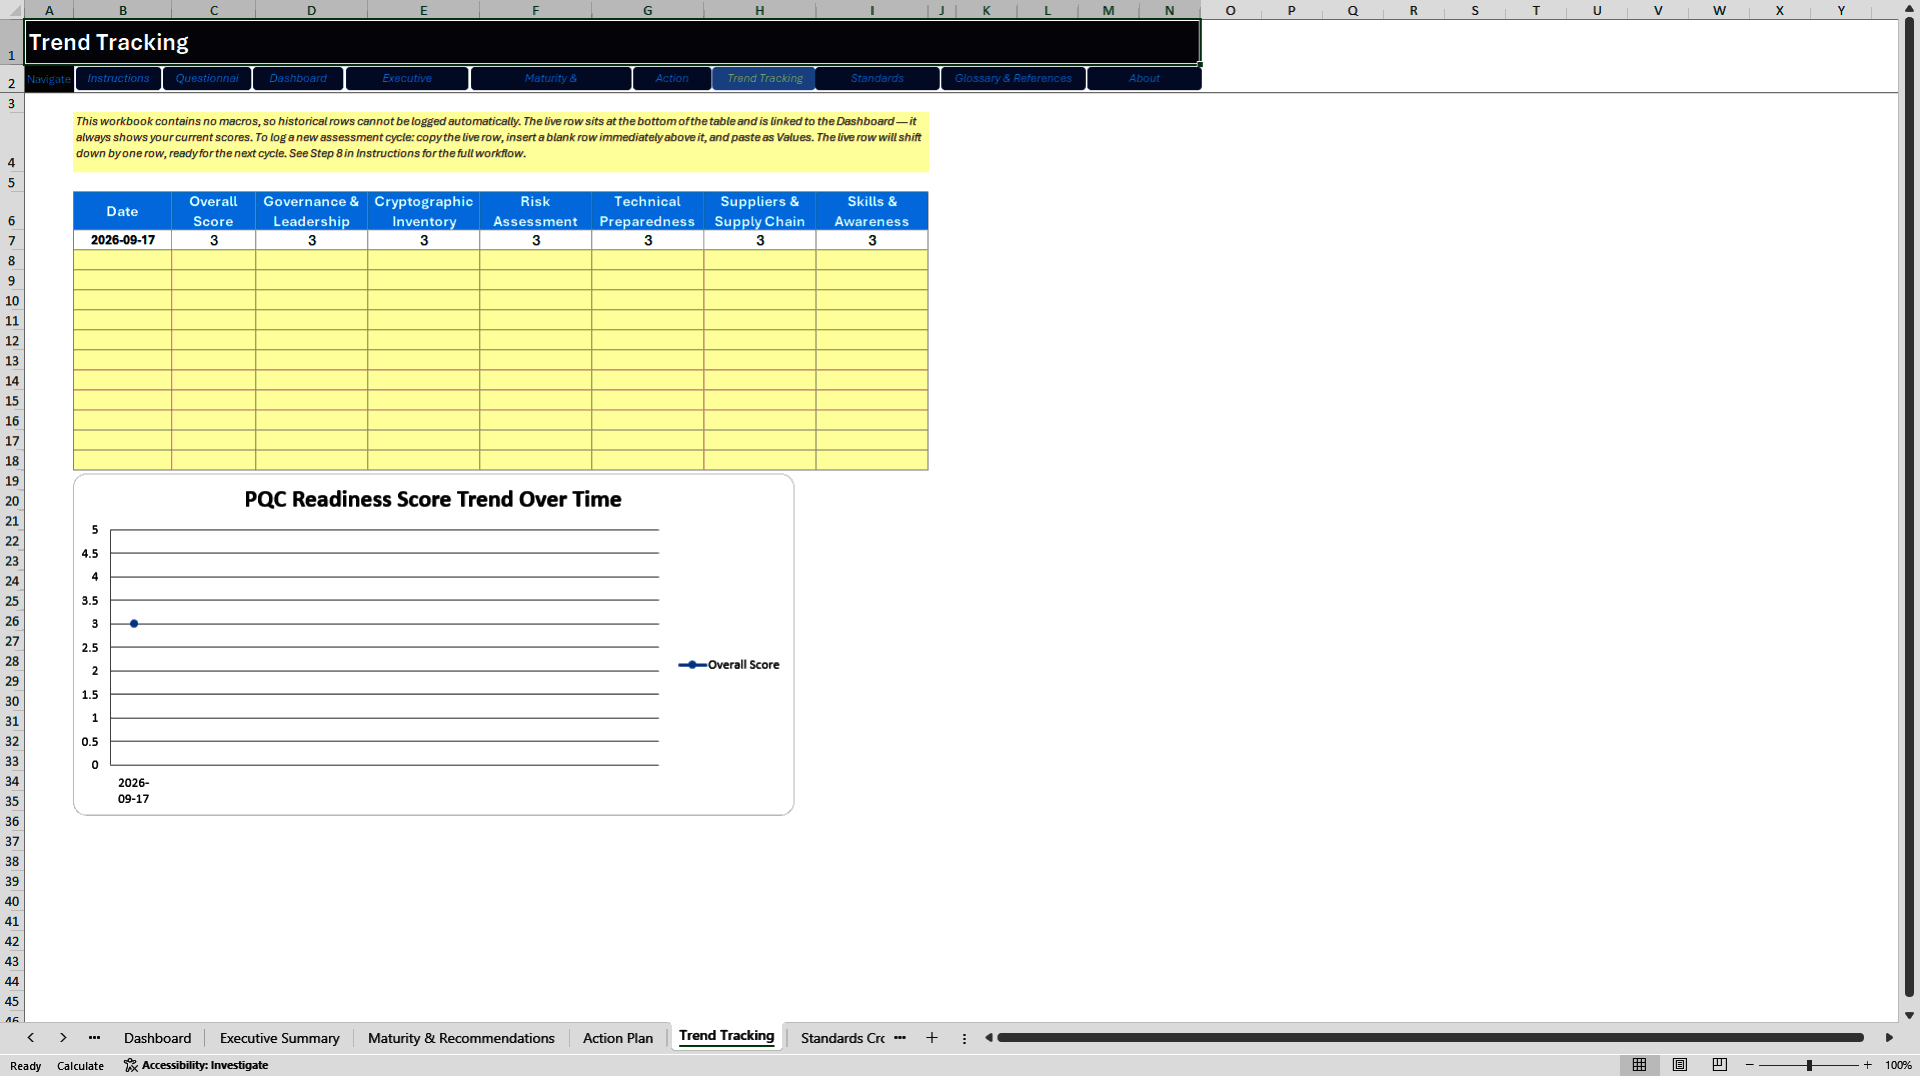
Built for Recurring Use – A Trend Tracking sheet with a live-linked baseline and a line chart lets you log scores every 6-12 months and show the board actual progress over time.
________________________________________
FREQUENTLY ASKED QUESTIONS
"What does using this tool actually look like, from start to finish?"
In one assessment cycle, you:
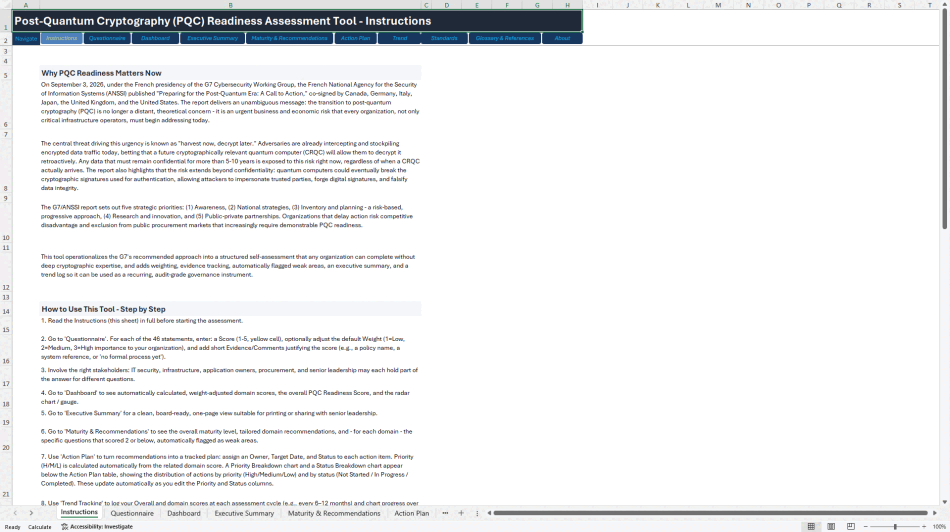
1. Complete the 46-question assessment – Score each item (1-5), optionally set weights based on your sector, and add evidence comments.
2. See your score instantly – The Dashboard auto-calculates your weighted Overall PQC Readiness Score and all 6 domain scores, with radar and gauge charts.
3. Get a board-ready summary – The Executive Summary sheet produces a printable one-pager with your score, maturity level, and auto-identified priority focus area.
4. See exactly what's missing – The Maturity sheet auto-flags weak questions (score ≤2) per domain, with tailored recommendations.
5. Build a tracked action plan – Every recommendation is pre-loaded with auto-calculated Priority, plus Owner, Target Date, and Status columns. Two live pie charts show progress at a glance.
6. Reuse the output for compliance – The Standards Crosswalk maps every answer to ISO 27001, DORA, NIS2, SOC 2, and HIPAA.
7. Log progress over time – Freeze your scores into the Trend Tracking sheet each cycle and watch your readiness climb.
You walk away with: a defensible score, a prioritized action plan with owners and deadlines, board-ready visuals, and audit-grade evidence – all in one macro-free Excel file.
"NIST, ANSSI, and ENISA already publish free PQC guidance – why would I pay for this?" Because those are narrative documents, not a scored tool. They tell you what to do; this operationalizes it into something you fill in once and get a weighted score, a dashboard, a flagged weak-area list, and a tracked action plan out of. If you want the free reading material first, we'd actually recommend it – read the underlying guidance, then use this tool as the operational layer that turns understanding into a repeatable, trackable process.
"Is the standards crosswalk a certified compliance mapping?" No, and we're upfront about that. It's an indicative mapping based on the actual published control, criteria, rule, and article text (fact-checked, not guessed) – not a certified Statement of Applicability, SOC 2 readiness opinion, HIPAA compliance determination, or DORA compliance determination. Validate it against your own ISMS owner, SOC 2 auditor, HIPAA privacy/security officer, DORA compliance function, or legal counsel before relying on it for a certification or attestation.
"Does this replace a professional cryptographic audit?" No. This is a structured self-assessment, not an independent audit, a penetration test, or legal advice. Organizations with elevated risk profiles should complement it with a professional, independent review.
"Is this only for large enterprises, or only for one sector?" Neither. All 46 questions are sector-neutral – any organization, any size, can use the same tool. The Sector Weighting Guide is an optional overlay for suggested emphasis, not a requirement, and not a restriction on who can use it.
"Can I customize the questions, weights, or recommendations?" Yes. The workbook is fully editable. Adjust weights, add your own evidence, rename domains, or extend the questionnaire – it's a scaffold, not a locked template.
"Does this include policy documents or a board presentation file?" Not in this listing. This is the Excel assessment tool plus a fully completed sample workbook. It does not include a separate Word policy document or PowerPoint deck.
________________________________________
⚠️ IMPORTANT NOTICE
This tool provides structured self-assessment guidance for informational and planning purposes. It does not constitute a professional cryptographic audit, penetration test, legal advice, or a certification of compliance with any law, regulation, or standard (including ISO/IEC 27001, DORA, NIS2, SOC 2, or HIPAA). The Standards Crosswalk is an indicative mapping based on publicly available control/criteria/rule text and should be validated by your own ISMS owner, auditor, privacy/security officer, or legal counsel before being relied upon for any certification, attestation, or regulatory submission.
________________________________________
WHAT YOU GET
PQC_Readiness_Assessment_Tool.xlsx (10 sheets, macro-free)
• Instructions – G7/ANSSI context, "harvest now, decrypt later" explainer, step-by-step usage guide, scoring scale, and weighting guidance
• Questionnaire – 46 questions across 6 domains, each with Score (1-5), Weight (1-3), Evidence/Comments, Regulatory Relevance tag, ISO 27001 mapping, NIS2 mapping, and DORA mapping
• Dashboard – Auto-calculated weighted domain and overall scores, color-coded ratings, a radar chart across domains, a two-ring gauge chart for the overall score, and the Sector Weighting Guide dropdown
• Executive Summary – Printable one-pager: org name/date fields, overall score, maturity level, domain scorecard, and an auto-identified priority focus area
• Maturity & Recommendations – Auto-computed maturity level (1-5) with tailored recommendations per domain and automatically flagged weak-scoring questions (score ≤2) per domain
• Action Plan – All recommendations pre-loaded with auto-calculated Priority plus editable Owner, Target Date, and Status (dropdown) columns, with live Priority Breakdown and Status Breakdown pie charts for at-a-glance executive reporting
• Trend Tracking – Live-linked baseline row, space for logging future assessment cycles, and a line chart of score progression over time
• Standards Crosswalk – Full-page reference mapping all 46 questions to ISO/IEC 27001:2022 Annex A, DORA (Regulation (EU) 2022/2554), NIS2 Article 21(2), SOC 2 Common Criteria, and HIPAA Security Rule provisions
• Glossary & References / About – Key PQC and compliance-framework terminology, source references, version history, and disclaimer
PQC_Readiness_Assessment_Tool_SAMPLE_COMPLETED.xlsx (bonus file)
A fully filled-in illustrative example (fictional mid-size financial services organization) showing realistic scores, weights, evidence notes, a completed Executive Summary, and a populated Action Plan – so you can see exactly what a finished assessment looks like before starting your own.
________________________________________
WHAT THIS TOOL IS
• A structured PQC self-assessment across 6 domains and 46 questions
• A weighted scoring engine with evidence tracking for auditability
• A board-reporting tool with an auto-generated executive summary
• A tracked action-planning tool with owners, dates, and status
• A cross-reference aid linking your PQC posture to ISO 27001, DORA, NIS2, SOC 2, and HIPAA
• A recurring-assessment tool with trend logging across cycles
WHAT THIS TOOL IS NOT
• Legal advice – see the Important Notice above
• A certified Statement of Applicability, SOC 2 opinion, or HIPAA compliance determination
• A substitute for a professional, independent cryptographic audit
• A guarantee of PQC migration or regulatory compliance
• A macro-driven or automated platform – all calculations are native Excel formulas; historical trend rows are logged manually each cycle
• A bundle including Word policy documents or a PowerPoint board deck – this listing is the Excel tool and completed sample only
________________________________________
WHO THIS IS FOR
• CISOs, Compliance Officers, and Information Security Managers starting or tracking a PQC transition program
• Internal Auditors and GRC Professionals who need a structured, evidence-backed assessment
• Consultants who need a repeatable PQC readiness engagement tool for client work
• Organizations of any size or sector – financial services, healthcare, government, critical infrastructure, technology, or general enterprise
• Organizations that already have an ISO 27001, DORA, NIS2, SOC 2, or HIPAA program and want to reuse existing evidence rather than start a parallel PQC assessment from zero
WHO THIS IS NOT FOR
• Organizations seeking an automated SaaS platform rather than an Excel-based self-assessment
• Organizations seeking a certified compliance audit or legal opinion
• Organizations that need policy documents or board presentation files as part of this specific purchase (not included in this listing)
________________________________________
THIS LISTING INCLUDES THE FOLLOWING FILES
• PQC_Readiness_Assessment_Tool.xlsx (10 sheets) – the complete, blank assessment tool
• PQC_Readiness_Assessment_Tool_SAMPLE_COMPLETED.xlsx – a fully filled-in illustrative example
WHAT THIS LISTING DOES NOT INCLUDE
This listing is for the PQC Readiness Assessment Tool only. It does not include a Word policy/procedures document, a PowerPoint board briefing deck, sector-specific question sets, a General Data Protection Regulation (GDPR) mapping, or ongoing/subscription support.
________________________________________
IMMEDIATE DOWNLOAD – You receive an editable Excel file (plus the completed sample). No macros, no scripts, no subscription fees. Own it forever.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in Maturity Model, Cyber Security Excel: Post-Quantum Cryptography Readiness Assessment Tool Excel (XLSX) Spreadsheet, Brahim Yahyaoui Consulting
ABOUT THE AUTHOR

I am a former CISO & Security Expert with 15+ years of hands‑on experience protecting critical infrastructures. Former Chief Information Security Officer at HPS, where I maintained ISO 27001 and PCI‑DSS certifications for National Payment Switch – the critical financial infrastructure that interconnects all local banks and processes national payment transactions.
I have led multiple
... [read more]
Ask the Author a Question
You must be logged in to contact the author.