 Click main image to view in full screen.
ISO 27001 Policy Starter Bundle with Annex A 2022 Mapping – Excel XLSX
Excel (XLSX) + Zip archive file (ZIP)


VIDEO DEMO
BENEFITS OF THIS DOWNLOADABLE EXCEL DOCUMENT
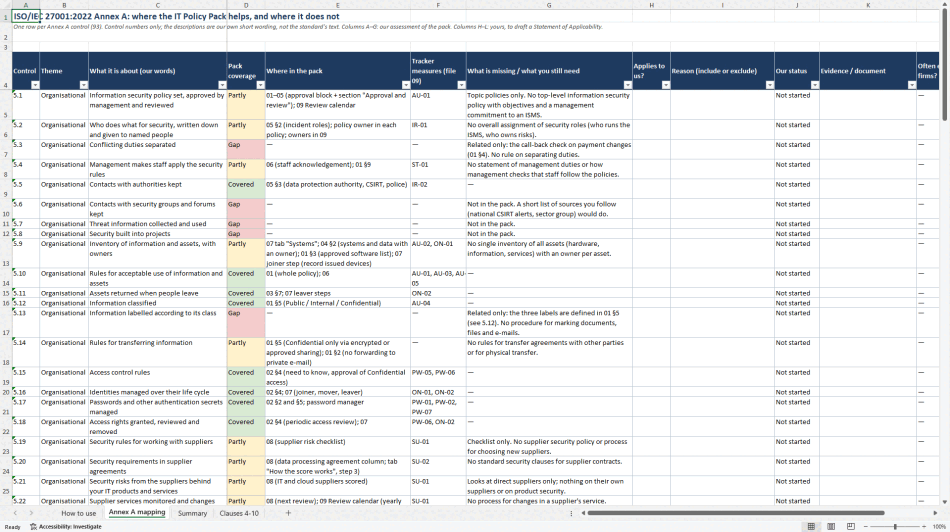
- See for all 93 ISO/IEC 27001:2022 Annex A controls whether the policies cover them, partly cover them or leave a gap, with what is still missing.
- Start your Statement of Applicability with columns for applicability, reason, status and evidence per control.
- Put five short, editable security policies and a 37-measure tracker in place, with owners and evidence, before your next audit or customer questionnaire.
ISO 27001 EXCEL DESCRIPTION
Short, editable IT and security policies for organisations with about 2 to 50 staff in the EU, plus a control-by-control map to ISO/IEC 27001:2022 Annex A. The map shows, for all 93 controls, where the policies help, where they help only partly, and where you still have a gap, so you know what to write next before a customer questionnaire or an audit.
What you get:
• Five policies (Word): acceptable use; passwords, MFA and access; remote work and own devices; backup and recovery; incident response plan.
• Staff one-pager (Word): the 12 rules on one page with an acknowledgement form.
• Three spreadsheets (Excel): joiner/mover/leaver checklist with a systems list; supplier risk checklist; implementation tracker with 37 measures, owners, evidence and a review calendar.
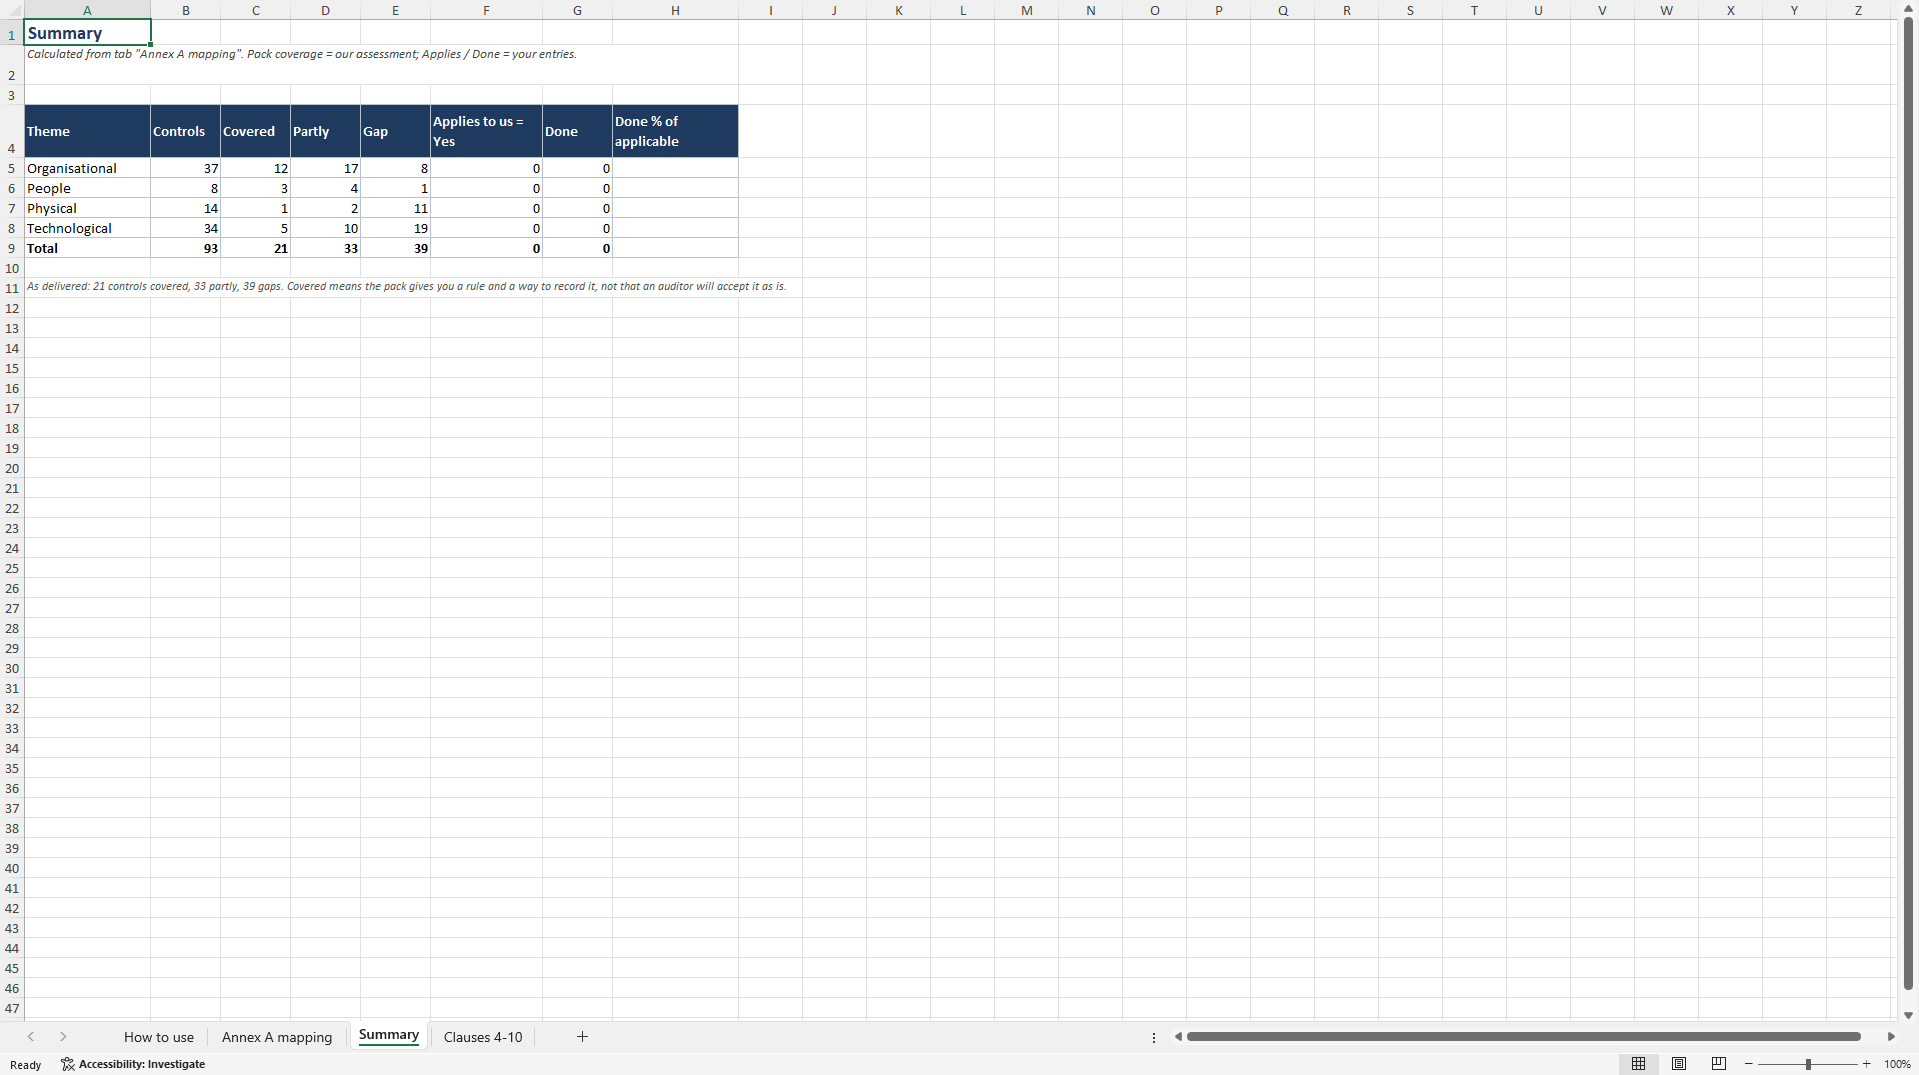
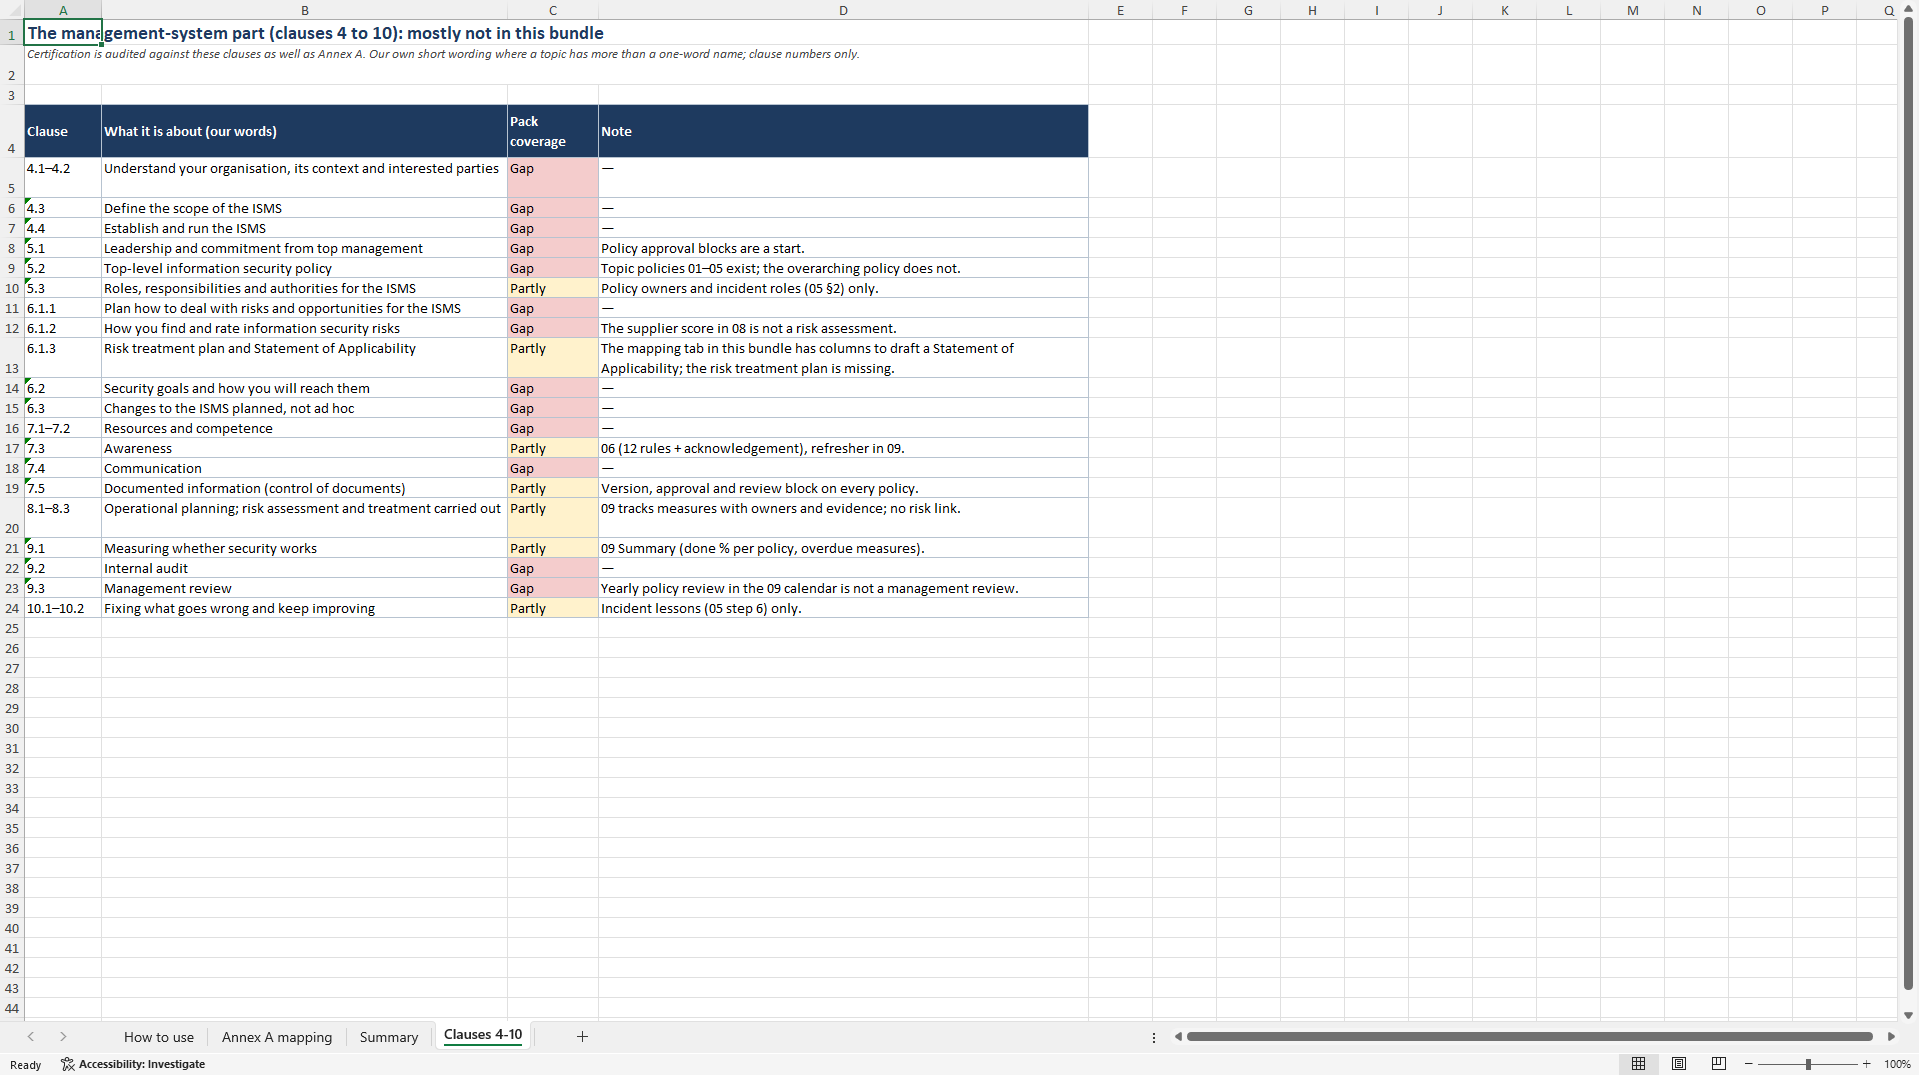
• Annex A mapping (Excel): all 93 controls of ISO/IEC 27001:2022 Annex A with coverage (Covered / Partly / Gap), the policy section and tracker measure that helps, what is still missing, and columns to draft your Statement of Applicability (applies? reason, status, evidence); a summary per theme; and a tab on clauses 4 to 10, the management-system part this bundle mostly does not cover.
• One-page action plan (PDF), two read-me files, and an AI-assistant folder with prompts to fill in the policies with Microsoft 365 Copilot, ChatGPT, Le Chat, Claude or Gemini.
Honest about the gaps. As delivered, the pack covers 21 of the 93 controls, covers 33 partly and leaves 39 open. Many of the open ones are physical-security and software-development controls that small cloud-based firms often exclude, with a reason. The workbook tells you which.
What it is not. Not a certification kit, and using it does not make you ISO/IEC 27001 certified or compliant: certification also needs a risk assessment, internal audit, management review and an accredited auditor. The standard's text is not included: control numbers only, with our own short descriptions (or a topic's plain name where it has only one, such as "Internal audit"). Not legal advice. Lerider Technologies is not affiliated with ISO or IEC.
Written for the EU (GDPR and NIS2 references, A4). Licence: one organisation, including its group companies.
Prepared with AI assistance under Lerider Technologies' direction, and checked against its cited sources before publication. A template, not legal advice.
Got a question about the product? Email us at support@flevy.com or ask the author directly by using the "Ask the Author a Question" form. If you cannot view the preview above this document description, go here to view the large preview instead.
Source: Best Practices in ISO 27001, Corporate Policies Excel: ISO 27001 Policy Starter Bundle with Annex A 2022 Mapping Excel (XLSX) Spreadsheet, Lerider Technologies




























